An assessor will compare your plan with what they see. A plan copied from a template describes a company that does not exist, and that shows within the first hour.
NIST SP 800-171 is the base for CMMC Level 2, and the system security plan is where you say how each requirement is met in your own building. It has to read like your building.
Walk it first
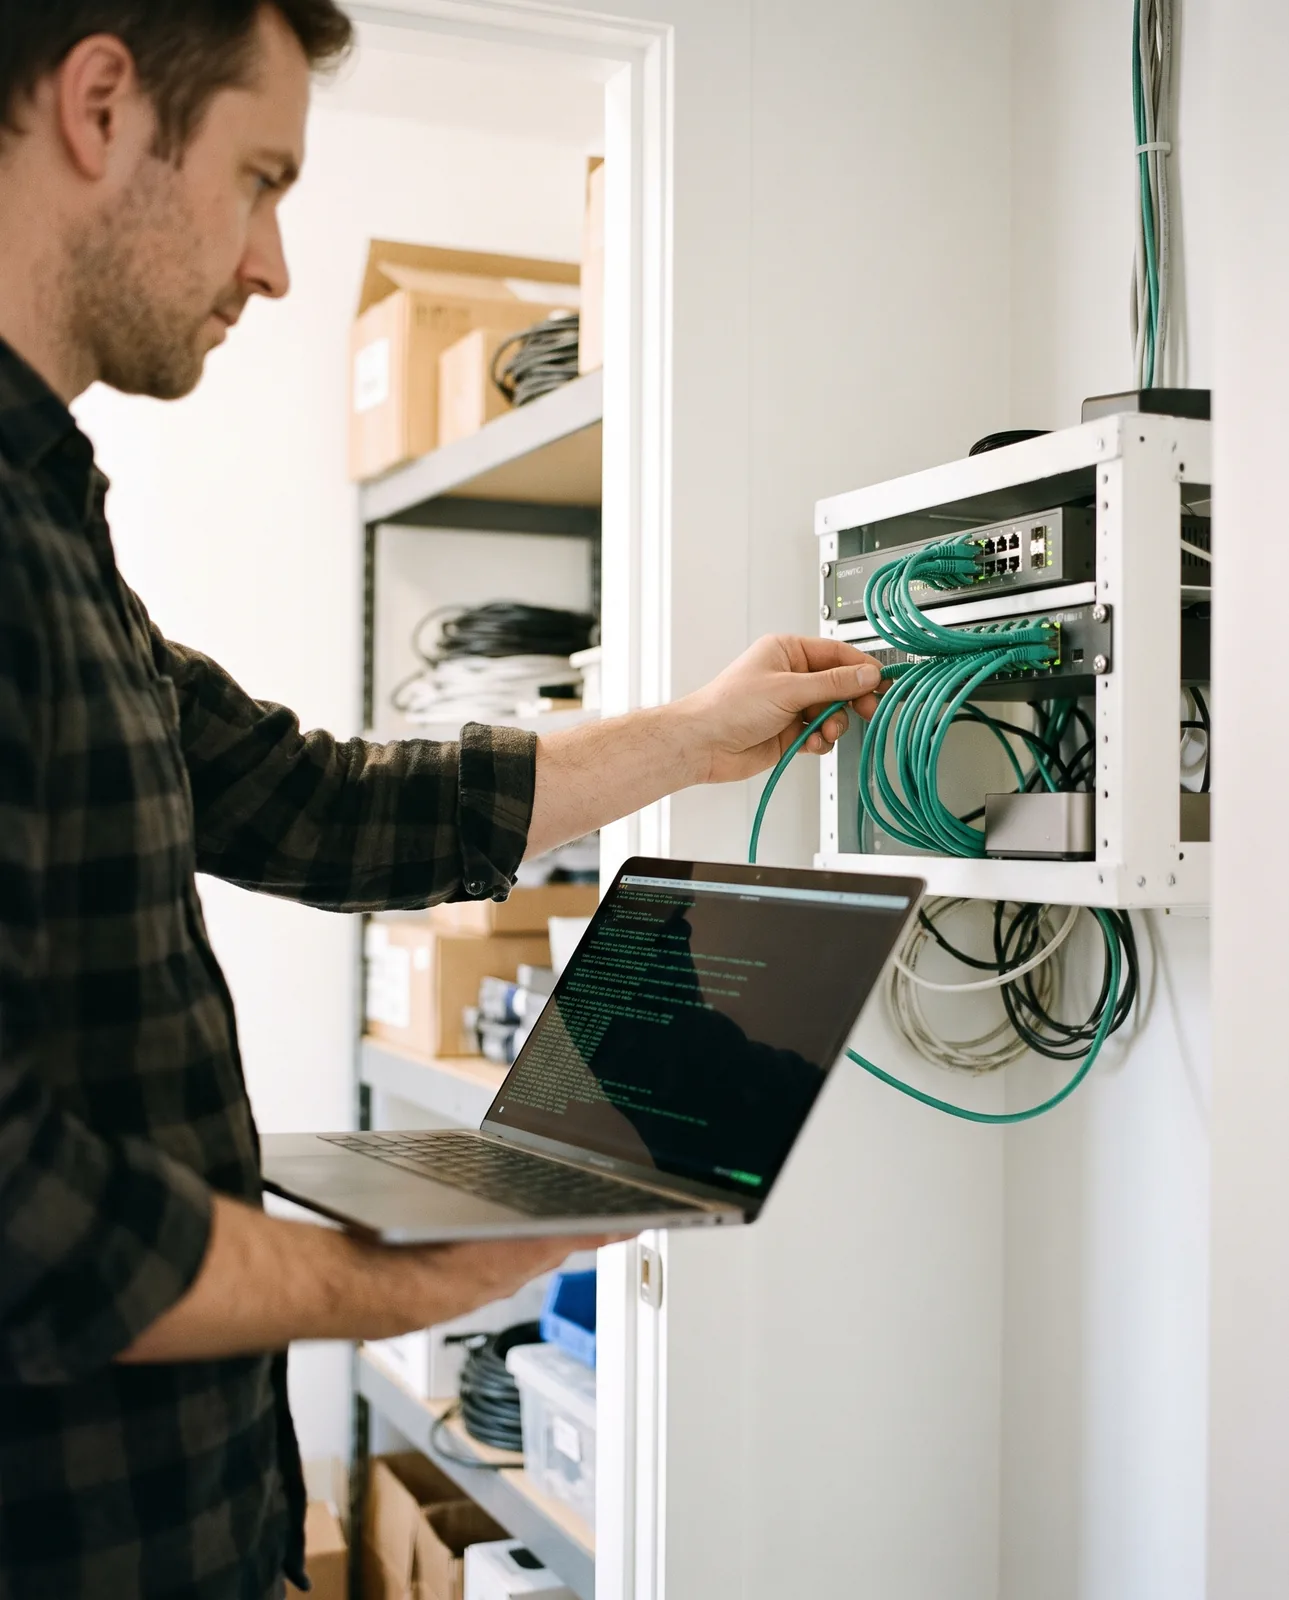
Take a laptop and go and look. Where does controlled unclassified information arrive? Which machine on the floor holds the drawings? Who has the keys to the wiring cabinet?
- Draw the boundary around the systems that handle it.
- Name the people who can reach those systems.
- Note the machines that cannot be patched, and why.
- Photograph nothing you would not show an assessor.
Write what is true, then fix what is missing. Never write what you hope will be true.
Gaps belong in the POA&M
If a requirement is not met yet, say so and put it in the plan of action with an owner and a date. An honest gap is something an assessor can work with. A false statement is a much larger problem for a defense supplier.
The first step
Pick one contract and trace its drawings from the email they arrived in to the machine that cuts the part. That path is the start of your boundary.