A path to customer data looks much the same in every sector. What changes is who asks about it, and how often.
We start with the data you hold and the people who check on it, then rank the map to answer them. Six sectors below, each with a sample case.
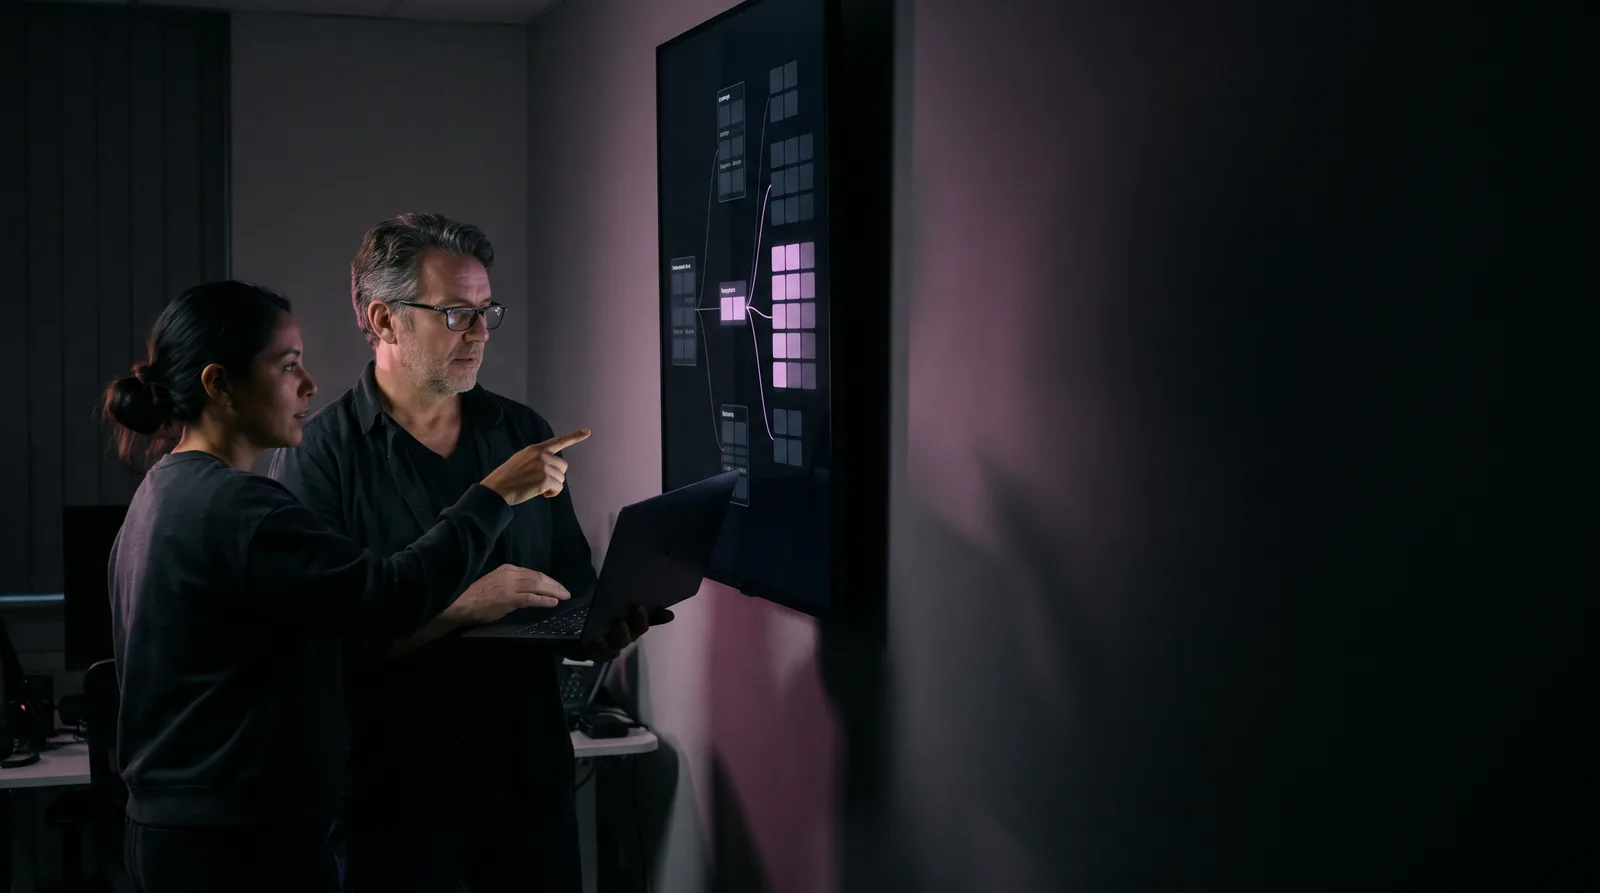
Marketplaces and carriers that grew by adding clouds. Three teams keep three lists, and the links between them belong to nobody.
Usually starts with trust links across clouds
Rule | What the map gives you |
NIS2 | A record of who holds access to what, for EU transport operators. |
GDPR | Evidence that confidentiality holds where you keep EU customer data. |
Online course platforms with shared clusters and a lot of add-ons. Each install can ask for more than it needs.
Usually starts with Kubernetes service accounts
Rule | What the map gives you |
SOC 2 | Who has logical access to each store, listed and dated. |
GDPR | Evidence that confidentiality holds where you keep EU learner data. |
Some rules ask for access controls outright, some leave the method to you. Either way, someone will ask who could read what, and on what date.
Card platforms and processors. A build role that can reach the card data store is the path that matters most.
Usually starts with deploy roles in AWS
Rule | What the map gives you |
PCI DSS | Who can reach cardholder data, and which of them need to. Every identity listed, with its long-lived keys and last use. A dated record to set beside your access logs. |
Software firms that hold patient records. Backups are copies of those records, with less supervision.
Usually starts with storage and backups
Rule | What the map gives you |
HIPAA Security Rule | An accurate risk analysis, with a map as its evidence. Who is authorized to reach each store of patient data, and proof that access stops there. |
Lenders, insurers and consumer finance apps. Examiners want a dated answer, and pipelines tend to hold the shortest paths.
Usually starts with pipeline tokens
Rule | What the map gives you |
GLBA Safeguards Rule | A periodic review of access controls, with dates. |
NYDFS Part 500 | Privileged accounts listed and reviewed, for firms licensed in New York. |
DORA | Identity and access evidence for EU financial entities. |
Studios and software firms usually hear this from a customer's security questionnaire, not a regulator. One dated report answers most of it, in place of a week of screenshots.
Usually starts with vendor roles
Rule | What the map gives you |
SOC 2 | Who was given access, changed or removed, and by whom. Configuration changes that opened a new path. |
ISO/IEC 27001 | Access rules and access rights, with a review date. |
Whatever your auditor asks for, the facts are the same: who could reach what, on which date, and what changed it.
Rule | What the map gives you |
CIS Benchmarks | Identity and storage settings, checked per account. |
SOC 2 | Dated access records for your auditor. |
ISO/IEC 27001 | Evidence for access control, mapped in the report. |
Plain summaries for orientation, not legal advice. Your auditor has the final word.