Most short paths to production start in a build. The token that ships your code often holds more than the job needs, because a narrower one once failed a deploy on a Friday.
Ask what happens if that token leaks through a log, a pull request from a fork, or a compromised action. The answer is whatever the token can reach, plus whatever those roles can reach.
Find out in an hour
- List every secret and role your pipelines use.
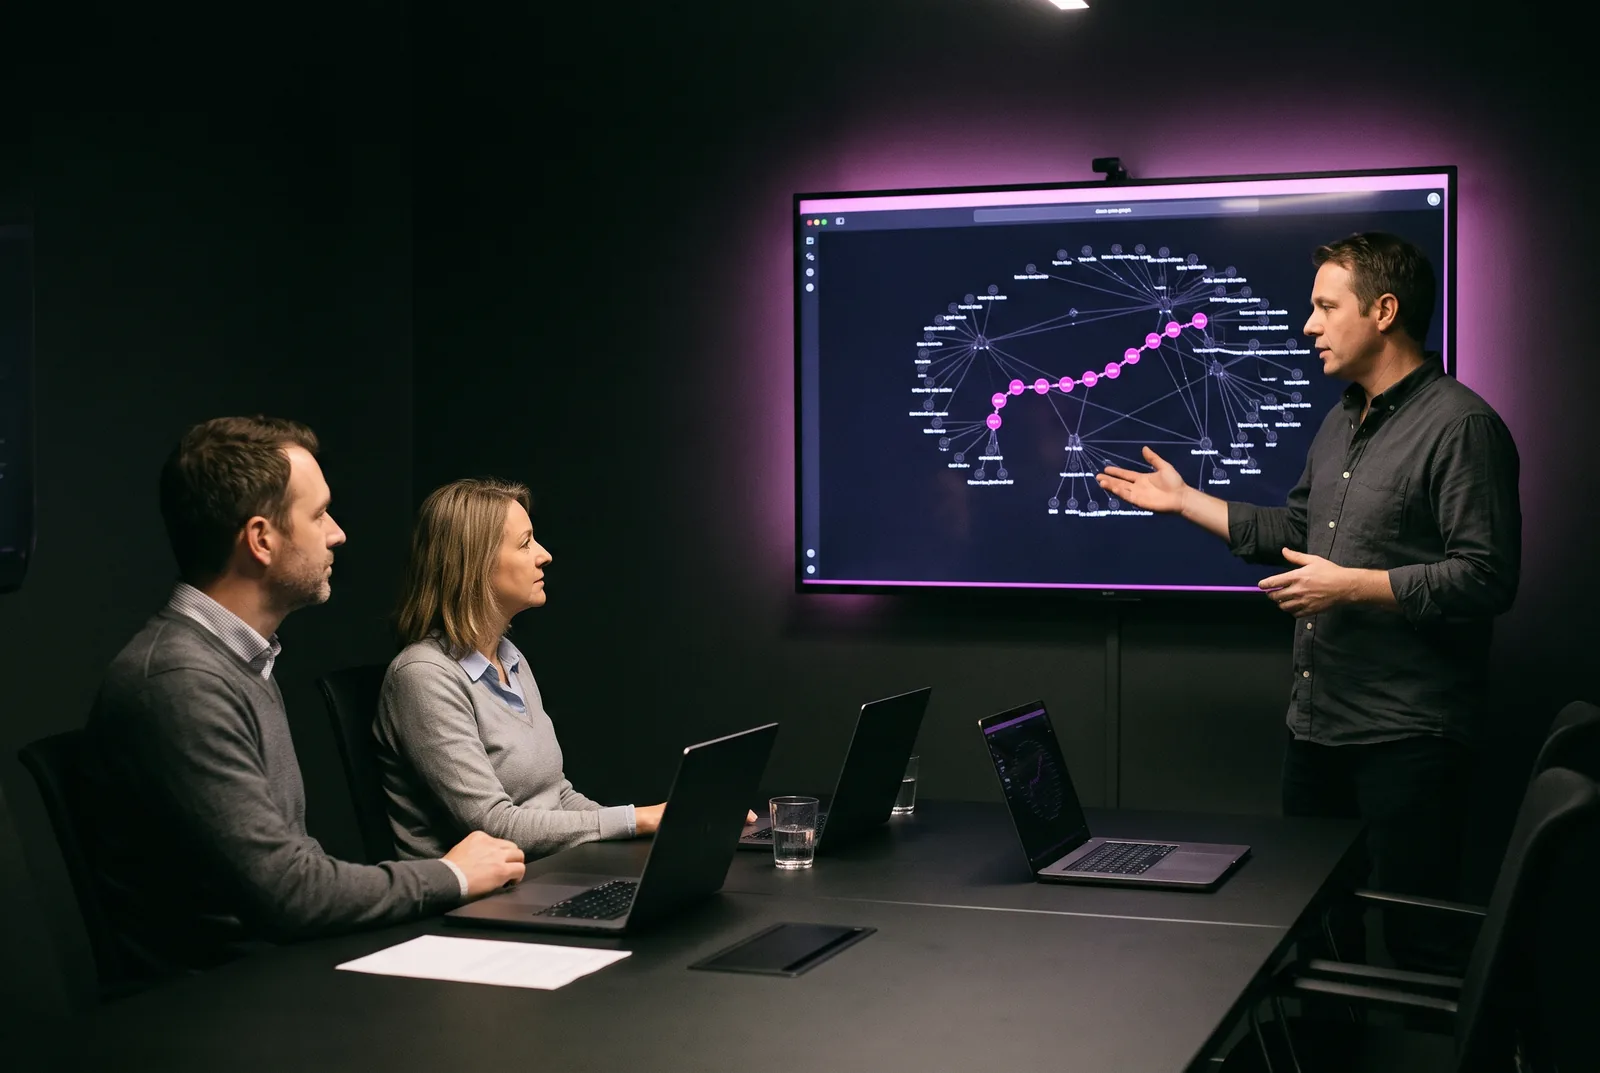
- Follow each one to the roles it can assume.
- Mark the first data store on each path.
- Sort by the shortest path to real data.
A build job does not need to read what it only needs to deploy.
The small fix
Split deploy from read. Use short-lived credentials issued per job, and limit them to one environment. It takes a few lines of Terraform, and it removes the path instead of watching it.