Every system that stores, processes or sends card data joins the assessment, and so does anything connected to it. A flat network can put the whole company in scope for the sake of one payment terminal.
A new tool rarely fixes that. Taking systems out of scope usually costs less, and it shortens every assessment after this one.
Three cuts to look at first
- Stop storing what you do not need. Old exports and call recordings are the usual finds.
- Move card entry to a hosted payment page or a validated terminal.
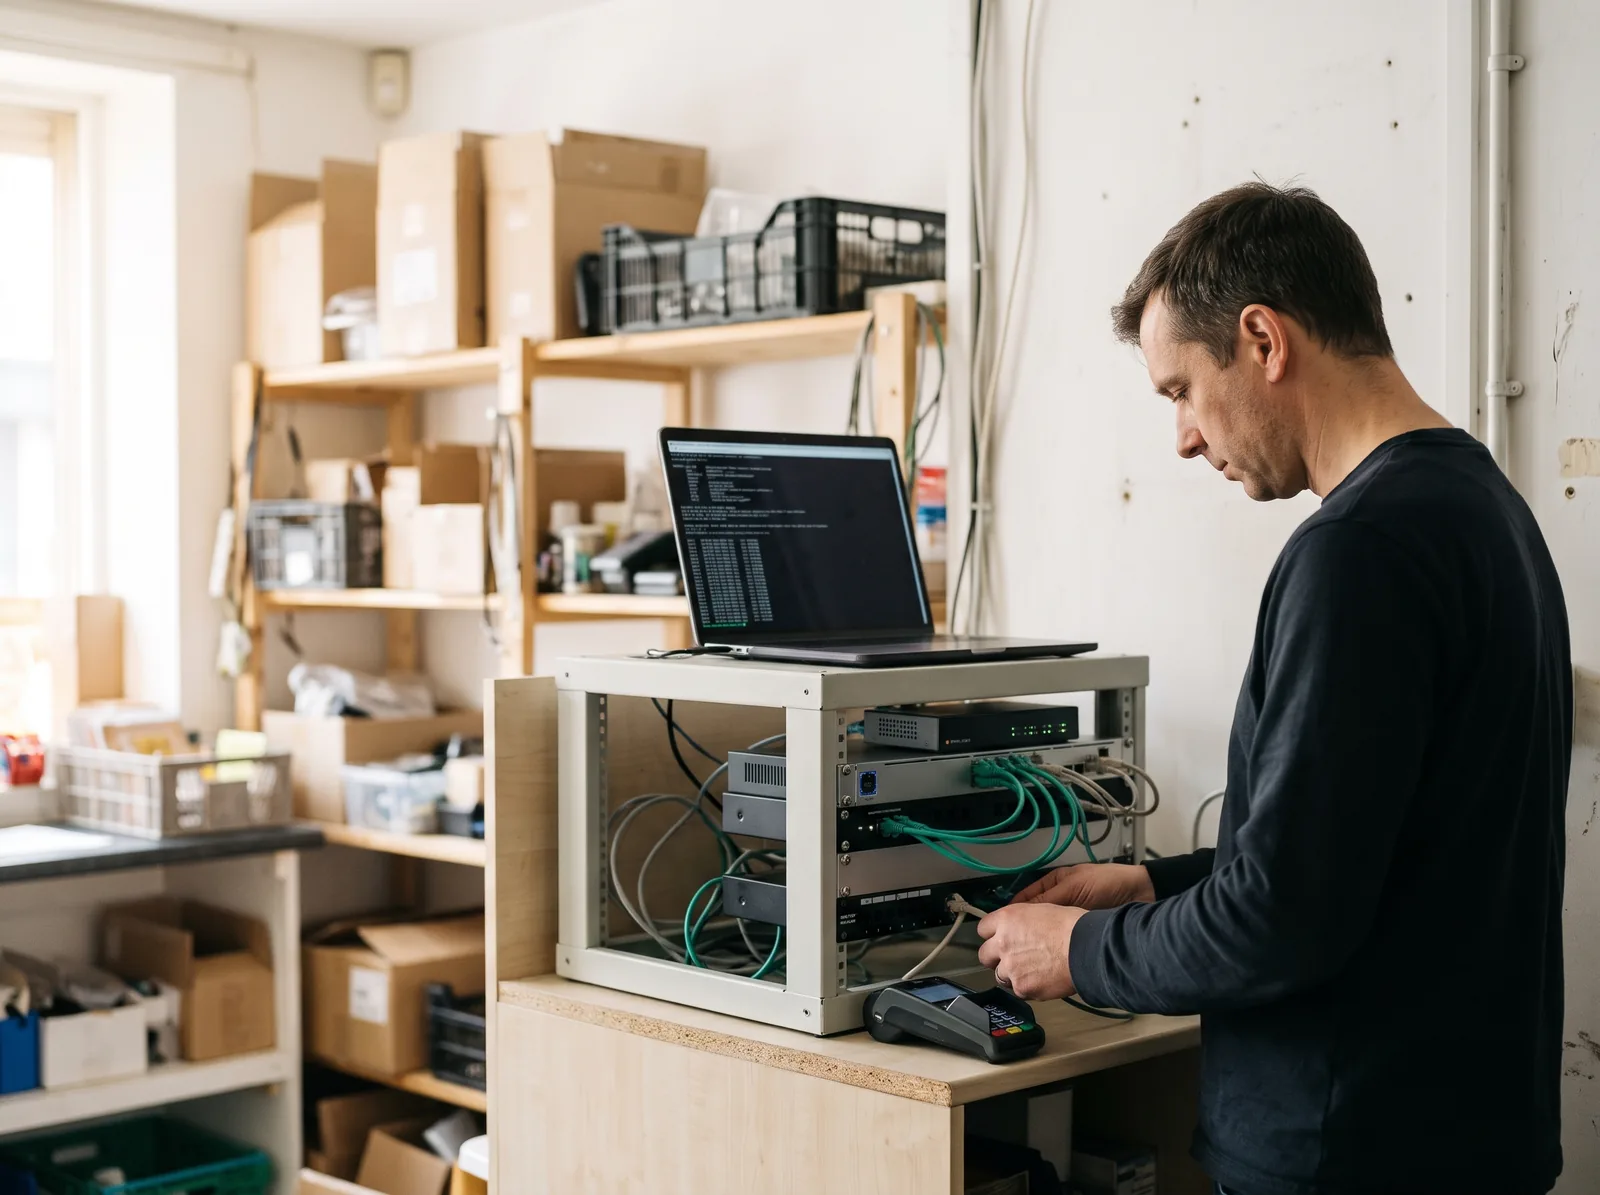
- Separate the card systems from the rest of the network, then test that separation.
The last one matters more than it sounds. Segmentation only counts if you can show it works, so plan the test at the same time as the change.
Each system you remove from scope is one you never have to explain again.
Check the payment page too
Version 4.0.1 asks merchants to keep an inventory of the scripts on their payment pages and to watch for changes. Marketing tags count. Agree who approves a new script before someone adds one on a Friday.
The first step
Draw how a card number moves through your business, from the customer to the bank. Mark every system it touches. Most teams find at least one they could retire.