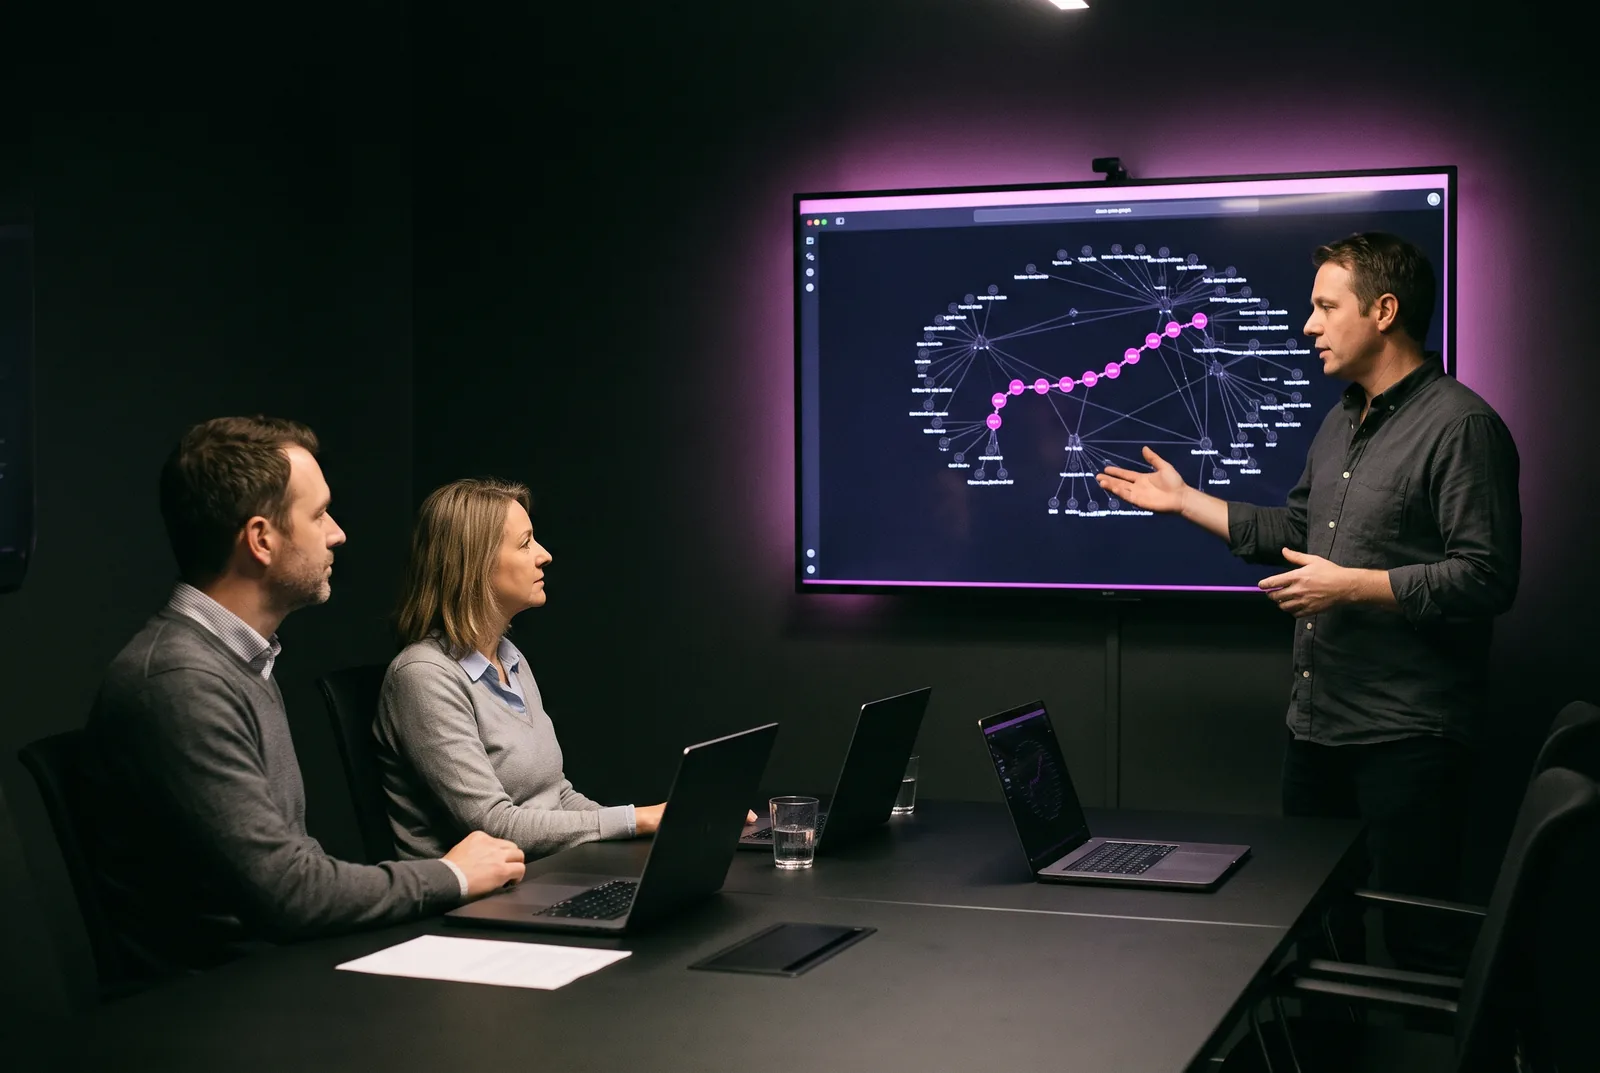
Identities, roles, trust links and data stores on one page, joined up the way an attacker would join them.
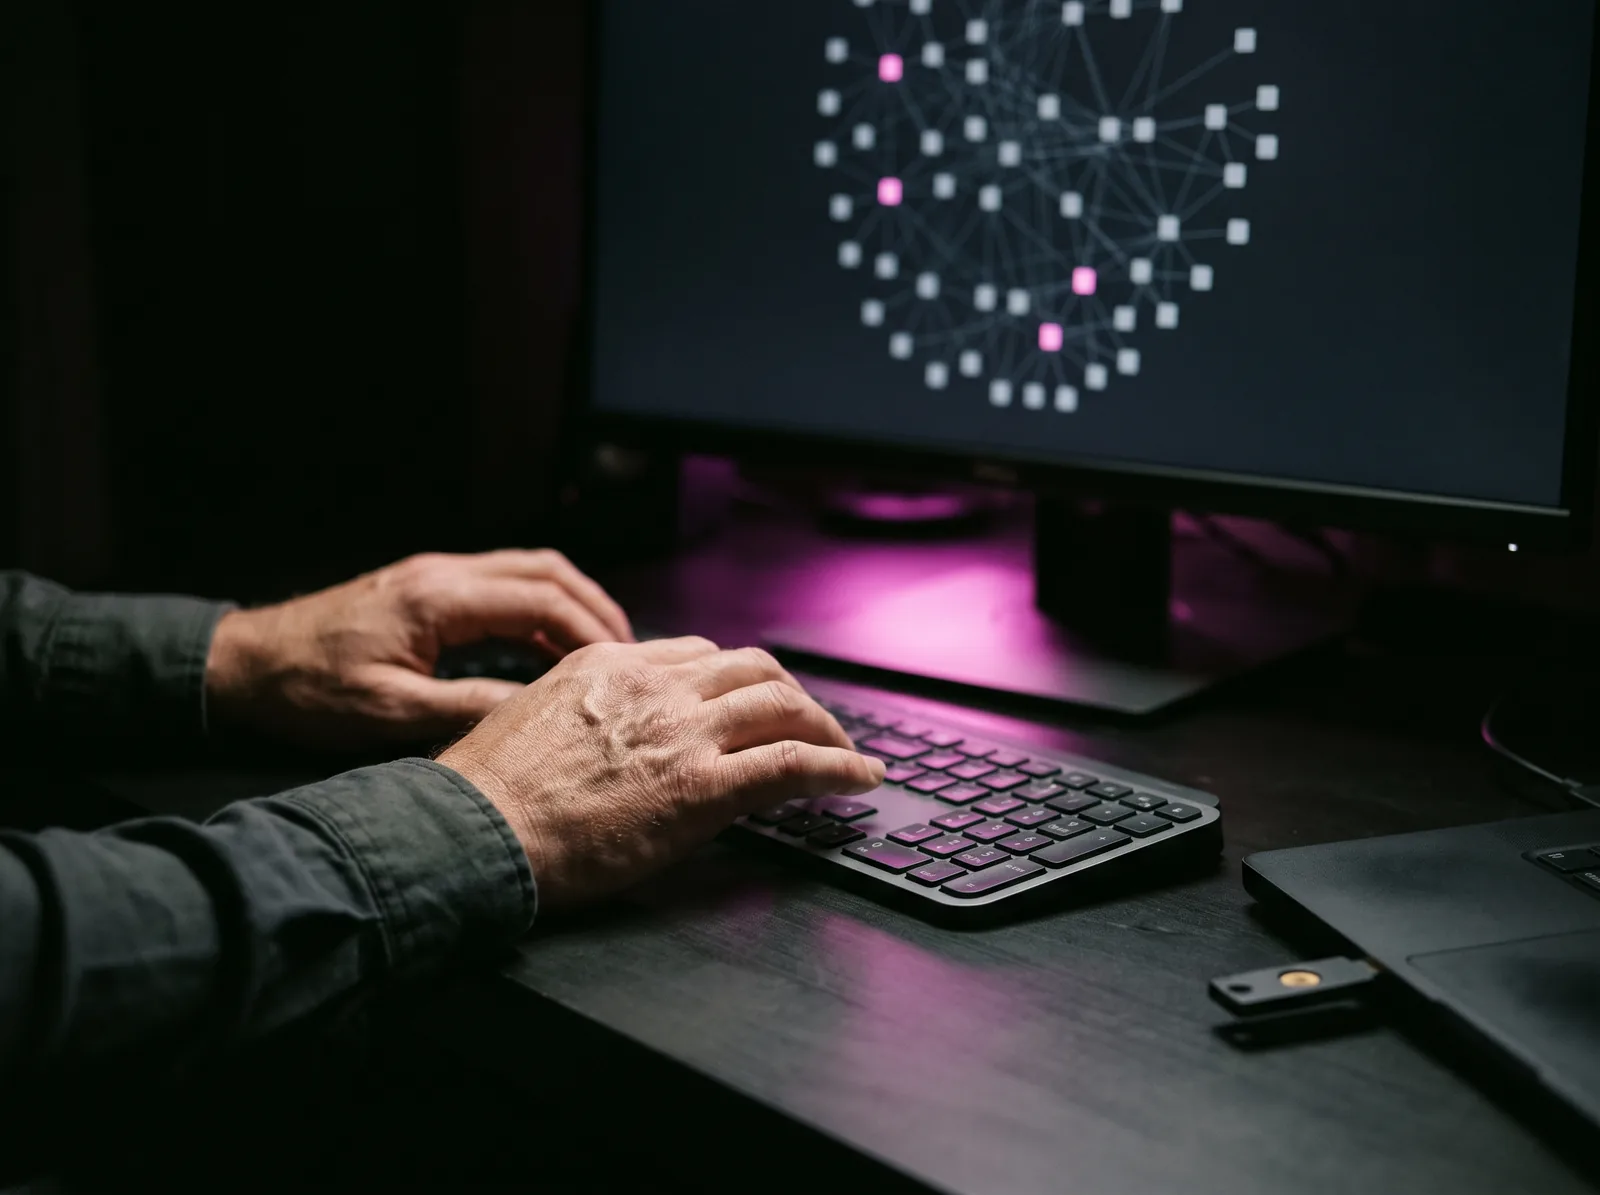
One read-only role, no agents, and a first map today. You can remove our access with one delete.
The map shows every path from an identity to your data, ranked by what it reaches. You start with the path that ends at customer records.
People, service accounts and the roles they can step into, including the ones nobody has used in a year.
The roles your builds and deploy tokens can step into. Most short paths to production start here.
Buckets, databases and keys, sorted by what is inside them and who can read it. File contents stay where they are.
The sample map holds 61 of them. They are the least reviewed part of most clouds, because no single team owns them.
Federated logins that carry a path from one provider into another.
Roles an outside company can assume, including suppliers you stopped using.
Service accounts with more reach than the workload they run.
Fixes arrive as small Terraform changes your team reviews and merges the usual way. Each one fixes one root cause and says how to roll it back.
You want to know | Start with | You get |
Who can reach customer records? | Reach map | Paths ranked by reach |
Which access keys have no owner? | Identity | Holders and last use |
What can a deploy token touch? | Pipelines | Every role it can step into |
Which stores hold regulated data? | Storage | Readers, counted in hops |
Which vendors can still get in? | Trust links | Each outside role, by name |
What will the auditor ask for? | Reports | CIS, SOC 2, ISO/IEC 27001 |
Add one role
We take inventory
Read the map
Fixes arrive
Free for one account. No card and no sales call. An engineer stays on hand while it runs.