Most admins use their rights for a few minutes a day and hold them all year. That gap is the risk: a stolen admin login works at any hour.
Timed sessions close the gap. A person asks, an owner approves, and access ends on its own.
How a session runs
- The admin asks for one role, for a set time.
- A named owner approves it.
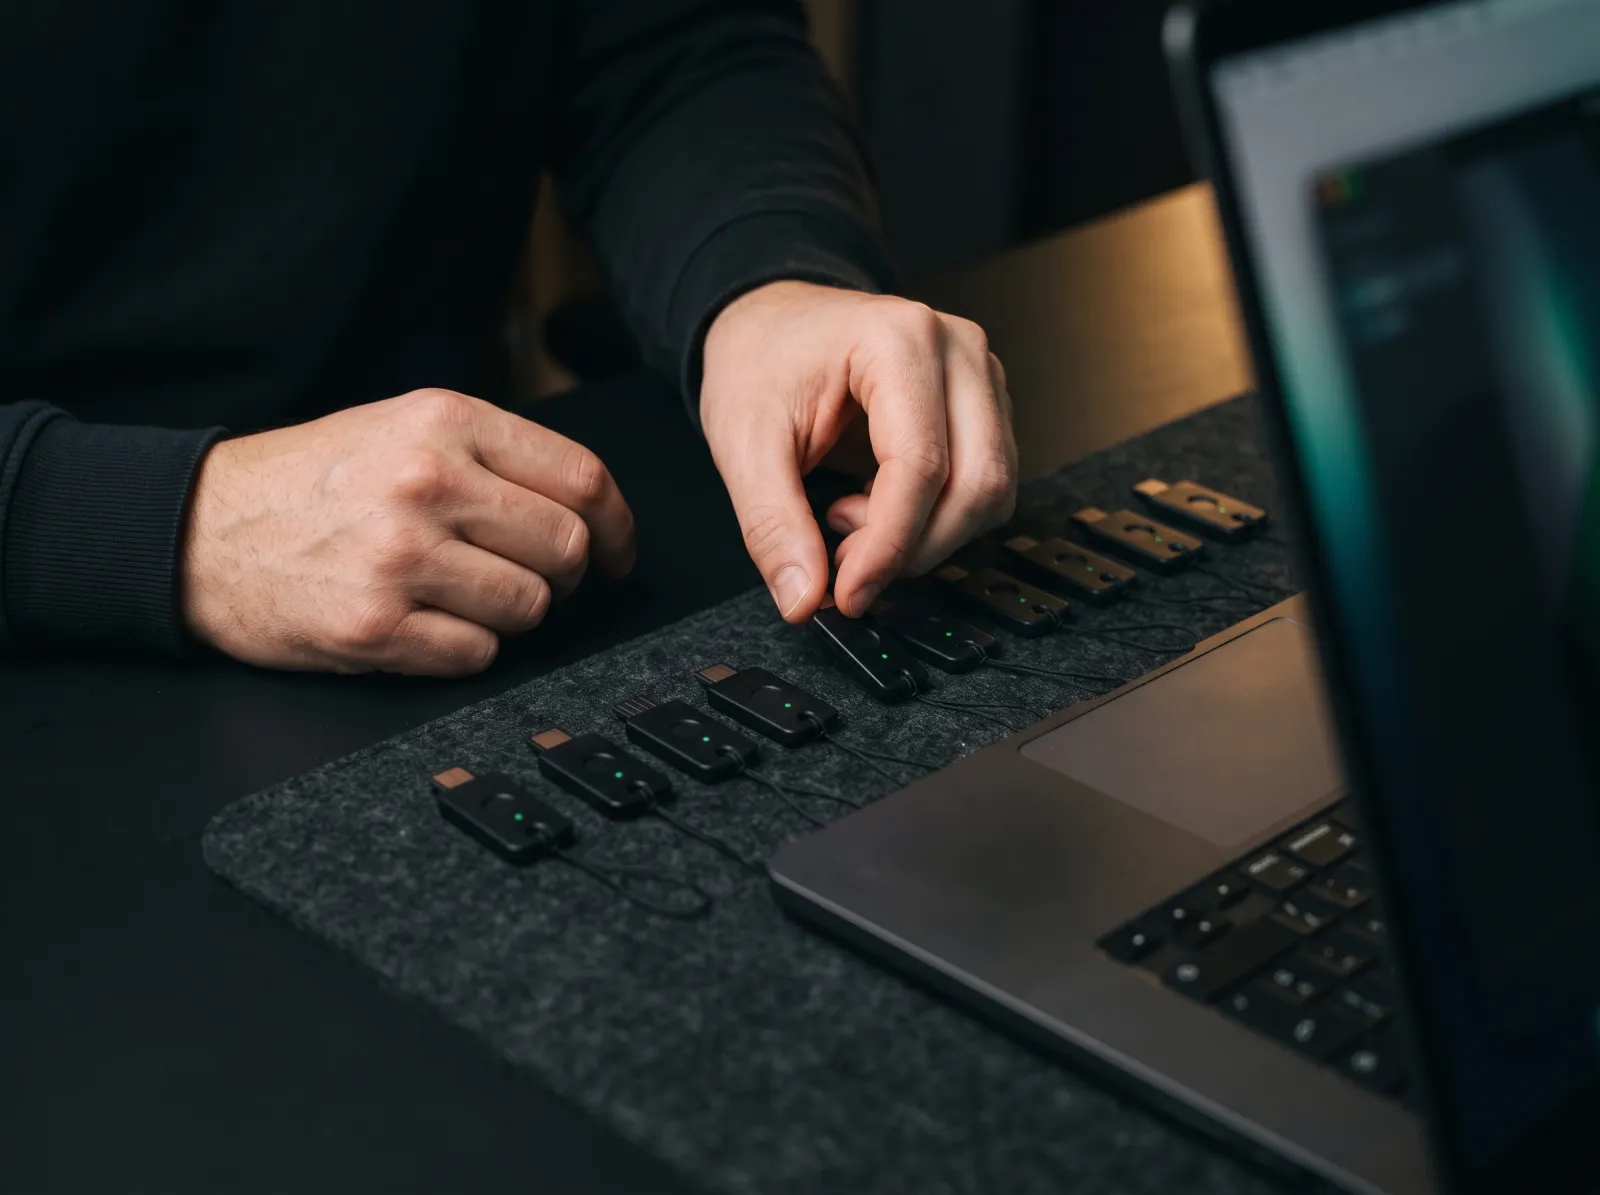
- A key tap opens the session, and activity is logged.
- Access ends on time, with no ticket.
If the access ends on its own, nobody has to remember to take it back.
The objection
Admins worry about the outage at 3 a.m. So agree a short list of emergency roles that approve themselves, and review every use the next morning. That list is usually three lines long.