Talk to sales +1-555-0187[email protected]
§1 IndustriesSample rule register
The record of accounts never changes. What changes is the list of rules behind it. Each review maps to the ones that apply to you.
§2 Four questionsSample rule register
A screenshot answers one of these, on one day. A closed review answers all four, for the whole period.
Who had access during the period?
Every account, role and path, with the last use beside it.
Who decided that they should?
A named owner on every row, never a shared inbox.
When was the decision made?
A date on every decision, from the signed review.
When did access end, if it was removed?
The time the app closed the account, not the time of the ticket.
§3 Regulated recordsHealthcare, finance, retail
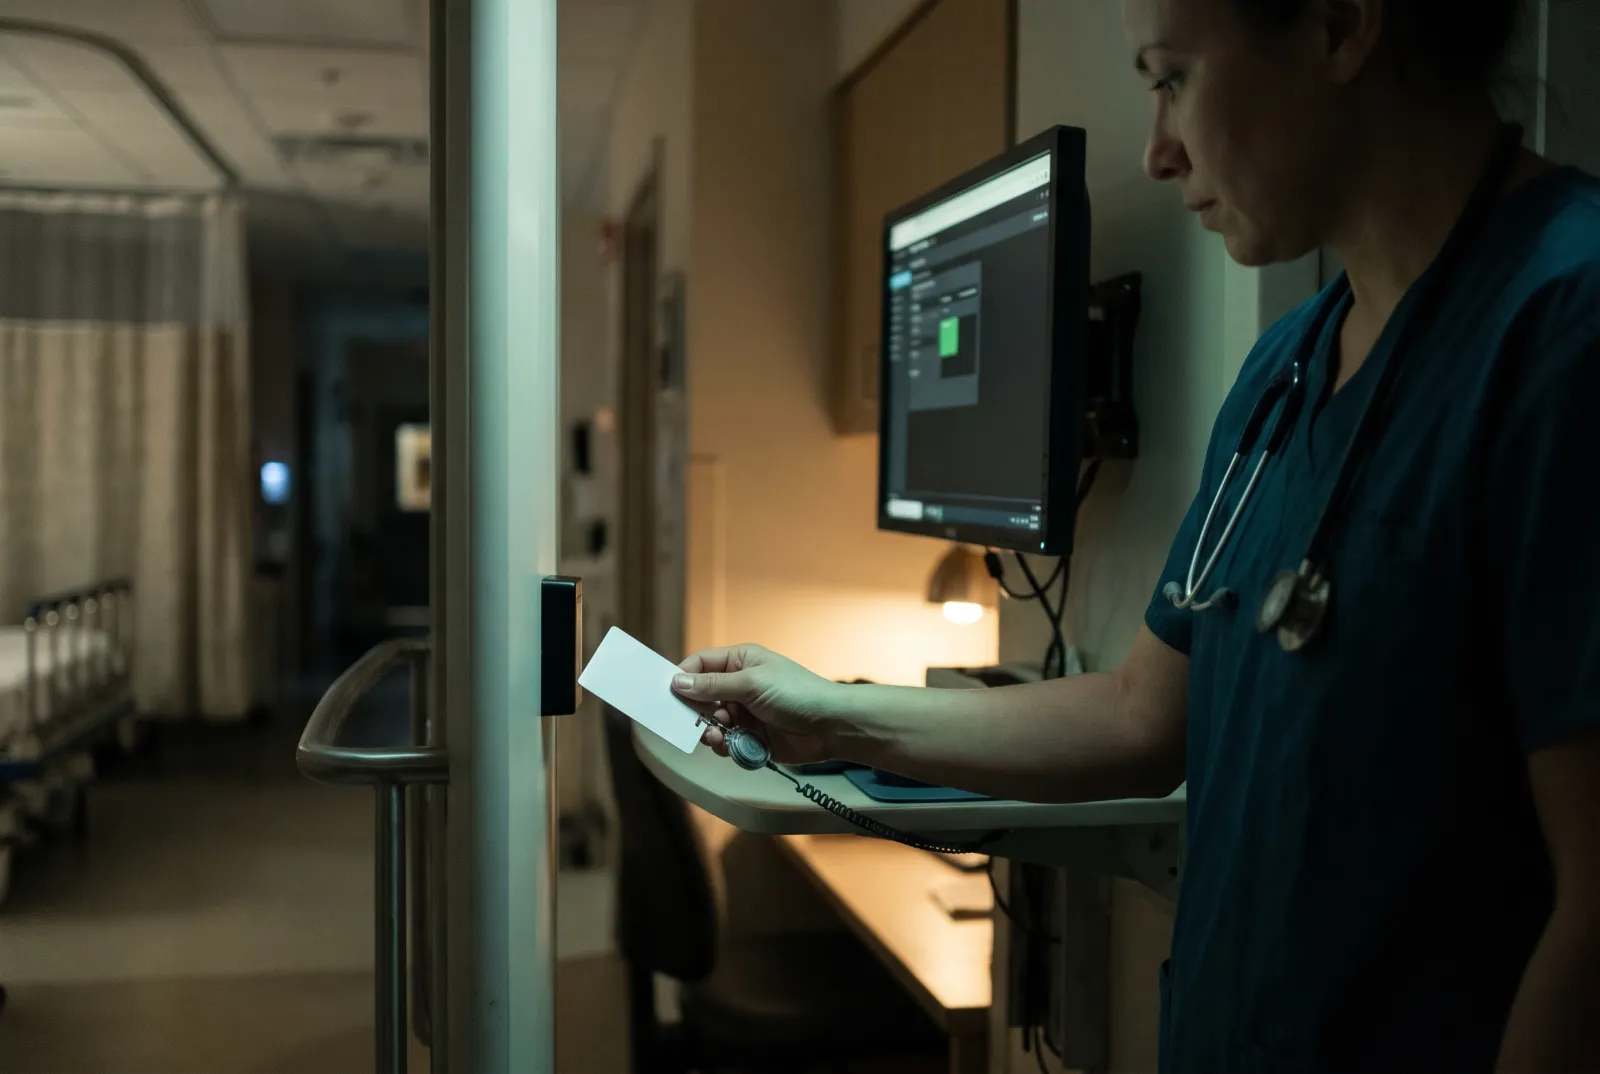
Patient charts, account numbers and card data each come with their own rules, and those rules ask who could open them. A closed review is the answer.
Clinic groups, hospital networks and the vendors that serve them. Staff move between sites, and access tends to stay behind.
HIPAA Security Rule | Who can open patient records, and ending that access when someone leaves. |
HIPAA technical safeguards | A unique login for each person, and proof of who signed in. |
HITECH Act | Extends HIPAA security duties to business associates. |
Credit unions, lenders and insurers. Examiners ask who can move money, and a shared login is not an answer.
GLBA Safeguards Rule | Access controls and multi-factor authentication for customer records. |
NYDFS Cybersecurity Regulation | New York rule for licensed firms. Access privileges and multi-factor authentication. |
DORA | ICT risk rules for EU financial firms, access management included. |
Stores, online sellers and anyone else who takes cards. Seasonal staff make the leaver list long.
PCI DSS | A card brand standard, set by contract, not a law. Covers least privilege and sign-in. |
GDPR | Applies if you hold personal data of people in the EU. Asks for secure processing. |
CCPA / CPRA | California customers. Reasonable security, with a right to sue after certain breaches. |
§4 Floors, firms and codeManufacturing, legal, technology
Your customers and clients often ask for this before any regulator does.
Shared terminals on the shop floor, and staff on three shifts. A badge sign-in gives each person their own record.
IEC 62443
Series for industrial control systems. Covers identification and use control.
NIS2
EU directive. Covers access control and multi-factor authentication.
NIST SP 800-171
US defense suppliers. Access control and authentication families.
Few statutes name law firms, but your bar duties and your clients' questionnaires do the same job.
ABA Model Rules: confidentiality
Reasonable efforts to prevent unauthorized access to client information.
ABA Model Rules: competence
Includes the risks of the technology you use.
Service accounts often outnumber the people who made them. Your customers still ask who owns each one.
SOC 2
Logical access, changes and removal.
ISO/IEC 27001:2022
Identity and access rights.
§5 End of registerSample rule register