Field Report No. 41, November 2026Incident response and threat research24/7 line +1-555-0187
§1 Lead report: sample case WL-26-114

The intruder stayed nineteen days. The logs kept every one.

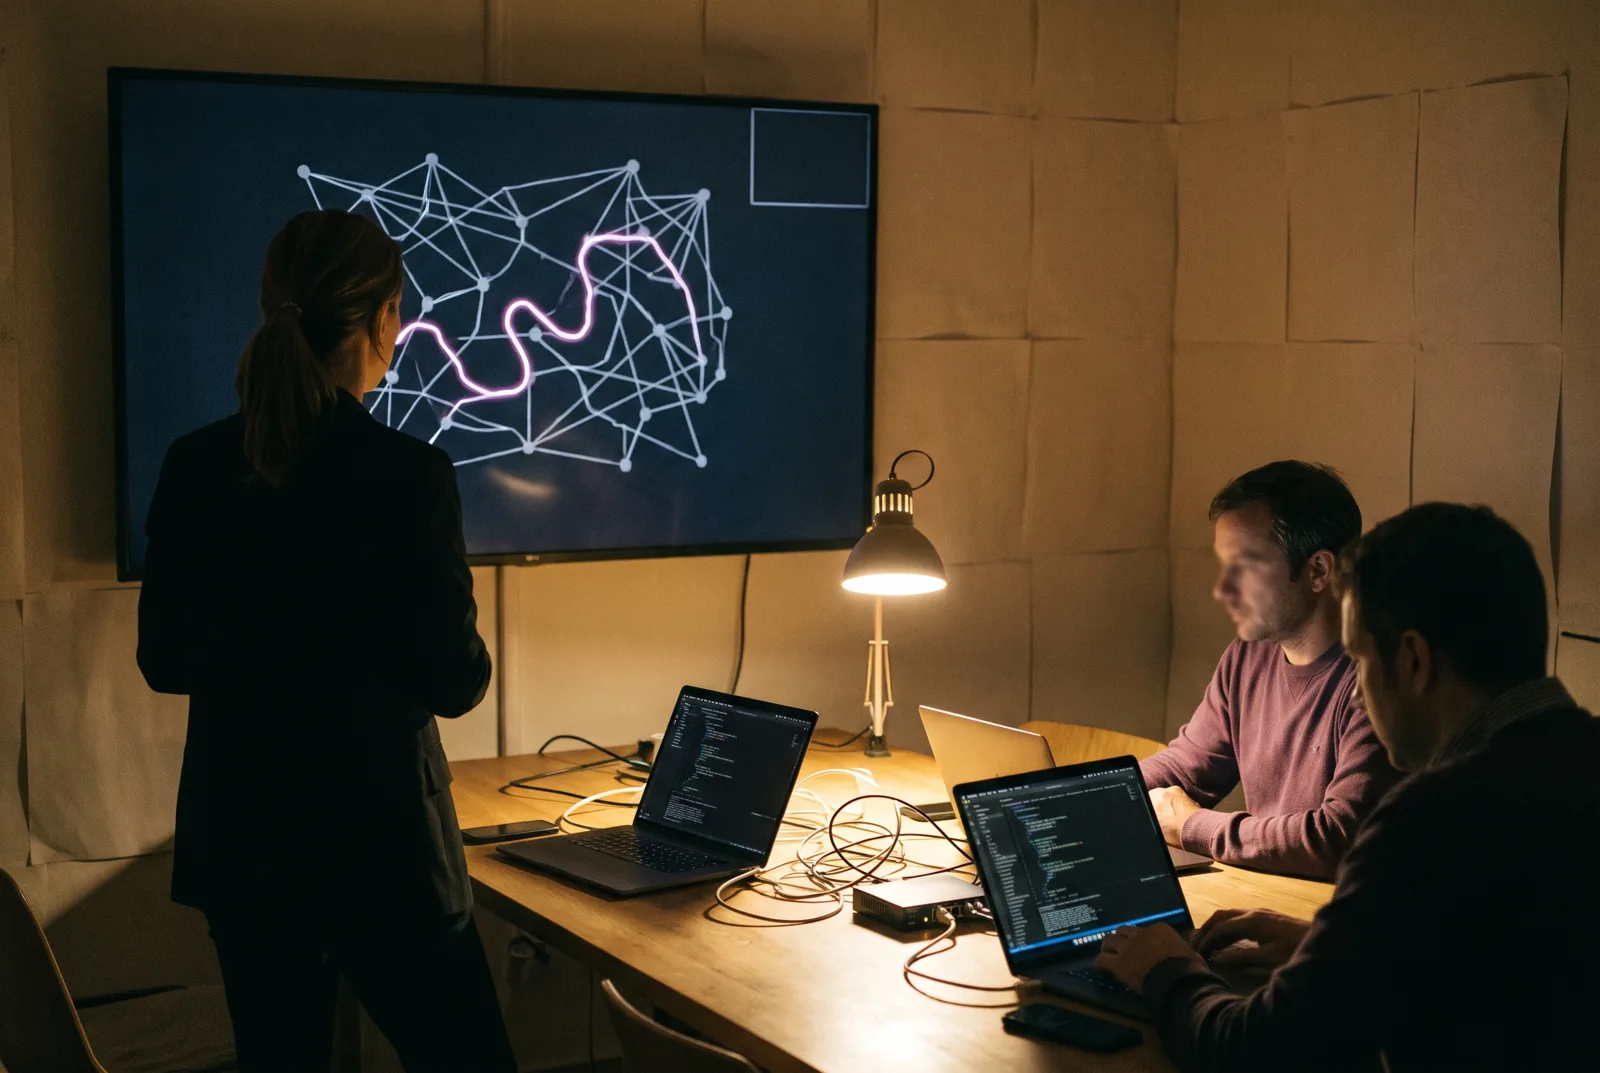
Responder at a wall display tracing an attack path while two colleagues work at laptops in an incident room at night
Report sheet WL-26-114
Sample

Client

Freight carrier, name withheld

Scope

412 hosts, 3 depots

Way in

Stale VPN account, user withheld

Findings

Critical 2 · High 5 · Low 11

Time to contain
4 h 12 min

Incident room, hour 31. Every host on the attack path gets a name and a time.

A freight carrier called on a Tuesday. By Friday it knew how they got in, what was touched and what to change first.
Briefs from the research desk

What a stolen session token still buys

Multi-factor stopped the password. It did nothing about the cookie that came after it.

Why we rebuild the timeline before we touch a host

Two events an hour apart can mean a stolen account. An average on a dashboard hides that gap.

Four log sources to keep for 90 days

What we ask for in the first hour of every case, and why cost is rarely the reason it is missing.
§2 If it is happening now, call the 24/7 incident line

A responder answers, not a queue. Tell us when you first noticed and who holds the network keys. Not urgent? [email protected]
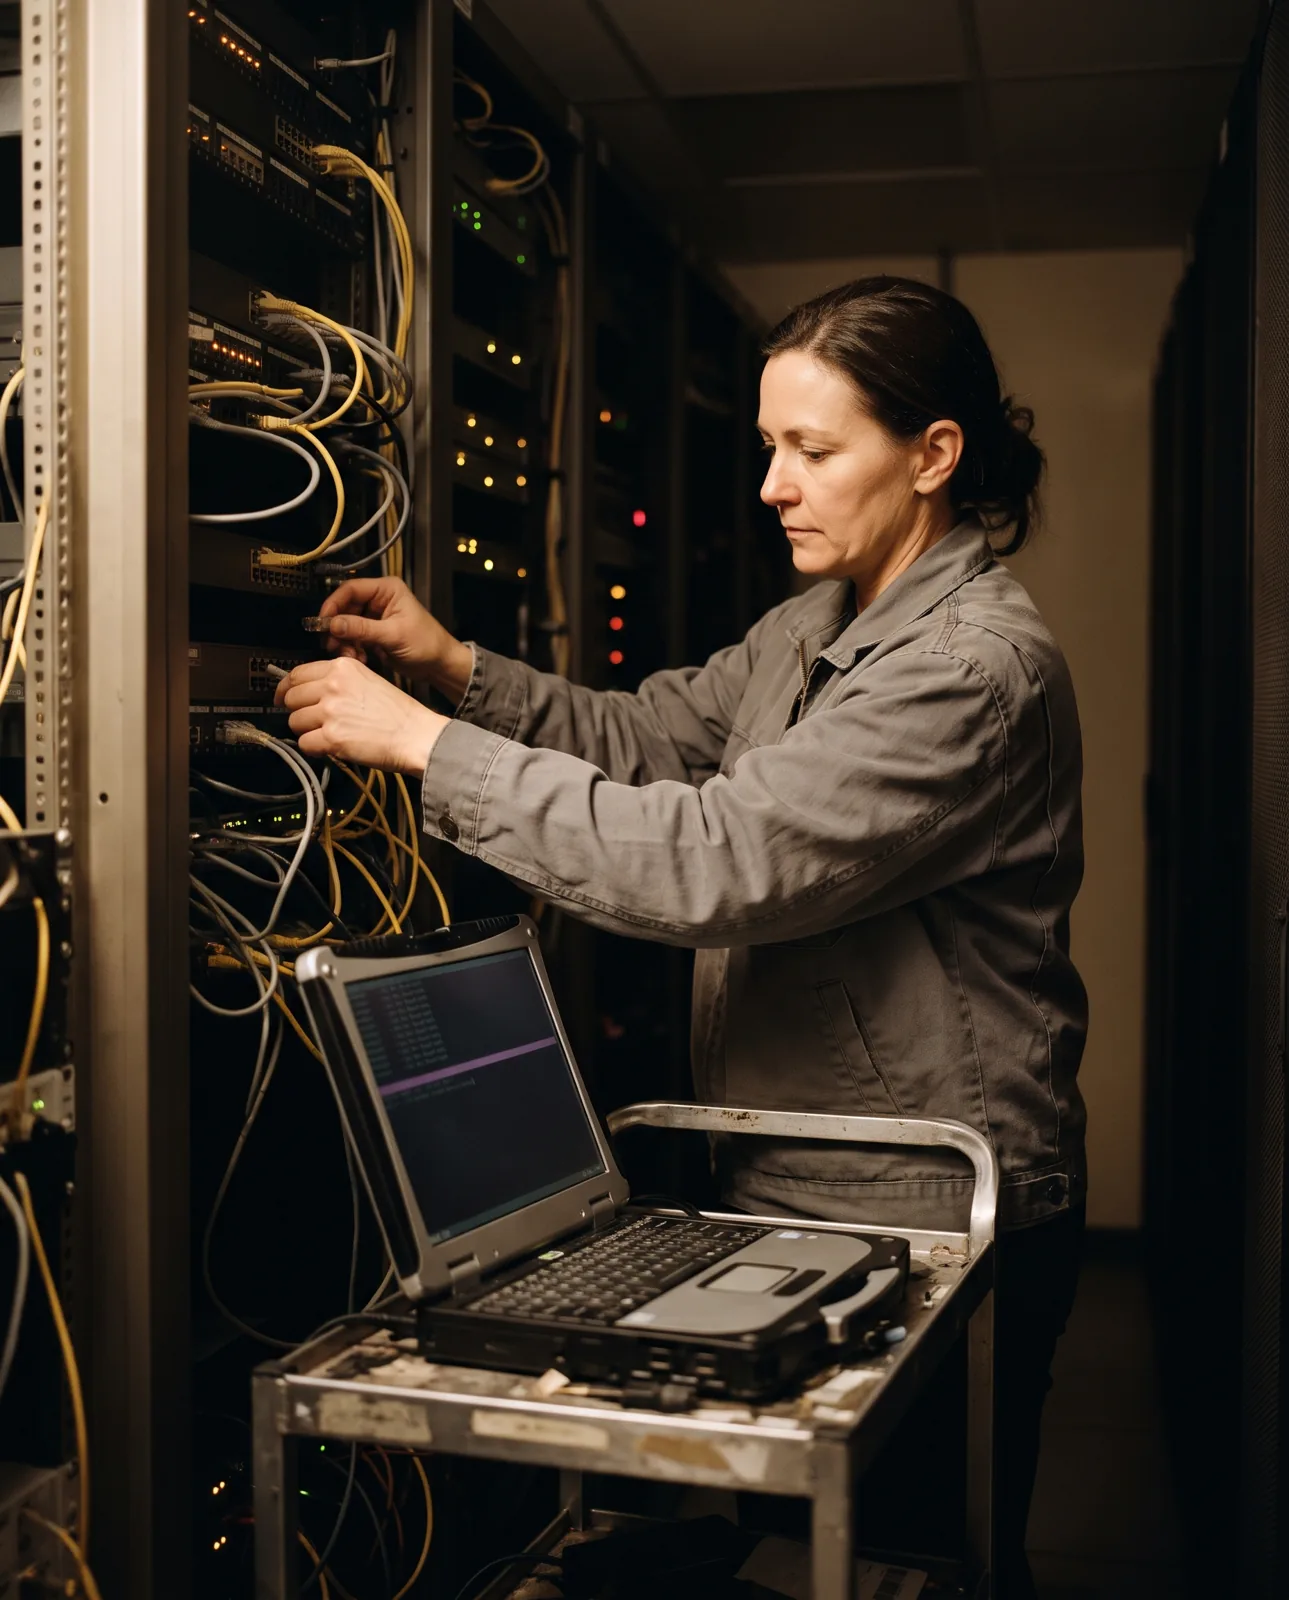
Field responder working at an open network rack, a laptop on a cart beside her
§3 Response stages

Four stages, one written record.

Every decision goes in the record as it is made, so the report at the end is the case itself, not a memory of it.

§3.1

Triage

First hour

Scope agreed, lead responder named.

§3.2

Contain

Same day

Stop the spread and keep the evidence intact.

§3.3

Investigate

Days 2–5

Rebuild the timeline from logs, disks and people.

§3.4

Report

Day 7

Findings by severity, what changed, what comes next.
Two analysts at a lab bench working through a suspect laptop, one pointing to a line on the screen
§4 Reports

Names come out. The facts stay in.

Every case we publish keeps its scope, severity counts and time to contain. Ask for one and judge the work before you ever need us.
Date
Sector
Finding
Severity
Contained in
Sep 2026
Healthcare group
Critical
3 h 40 min
Sample cases for this demo. Severity is the worst finding in each report.
Hands connecting a solid-state drive to a forensic imaging device wired to a laptop
§5 Evidence

Copied and hashed before anyone looks.

We work from verified copies, so the original stays as it was found. If your lawyer or insurer asks later, the log answers.

Evidence log WL-26-114
Demo sample

Item

Source

SHA-256

Logged

E-01

Depot file server, disk image

9f3c hash withheld

14:07

E-02

VPN gateway, 90 days of logs

a71e hash withheld

15:32

E-03

Dispatcher laptop, memory capture

04bd hash withheld

16:48

E-04

Mail tenant, audit export

c2e8 hash withheld

18:15

Two threat researchers at a night desk with disassembly graphs on dark monitors and a test laptop unplugged from the network
§6 Team

The person who answers stays to the end.

No handoffs to a second tier. Your lead responder writes the first note and signs the last page.
Incident response lead at a dark terminal with a phone headset around her neck

Incident lead

GCFA, CISSP

Forensic analyst

GCFE, GCFA

Threat researcher

GREM

Field responder

GCIH

Sample team for this demo.
§7 Contact

Tell us when you first noticed.

On-call responder taking a call on a headset at a night desk, a network graph on the monitor behind him
24/7 incident line
Email
Office

1180 Harbor Row, Suite 40, Portside, WA 98000-0000

New case note · Goes to the on-call lead