This page lists what we hold, how evidence moves and what we keep. Wardline is a fictional business, so every certificate below is a demo sample and none has been issued.
Copies on request, under NDA
Evidence handling and case systems
2026 to 2029
Security and confidentiality criteria
12 months to Jun 2026
Response and forensic work
Renewed yearly
Everyone who touches evidence
At hire, then yearly
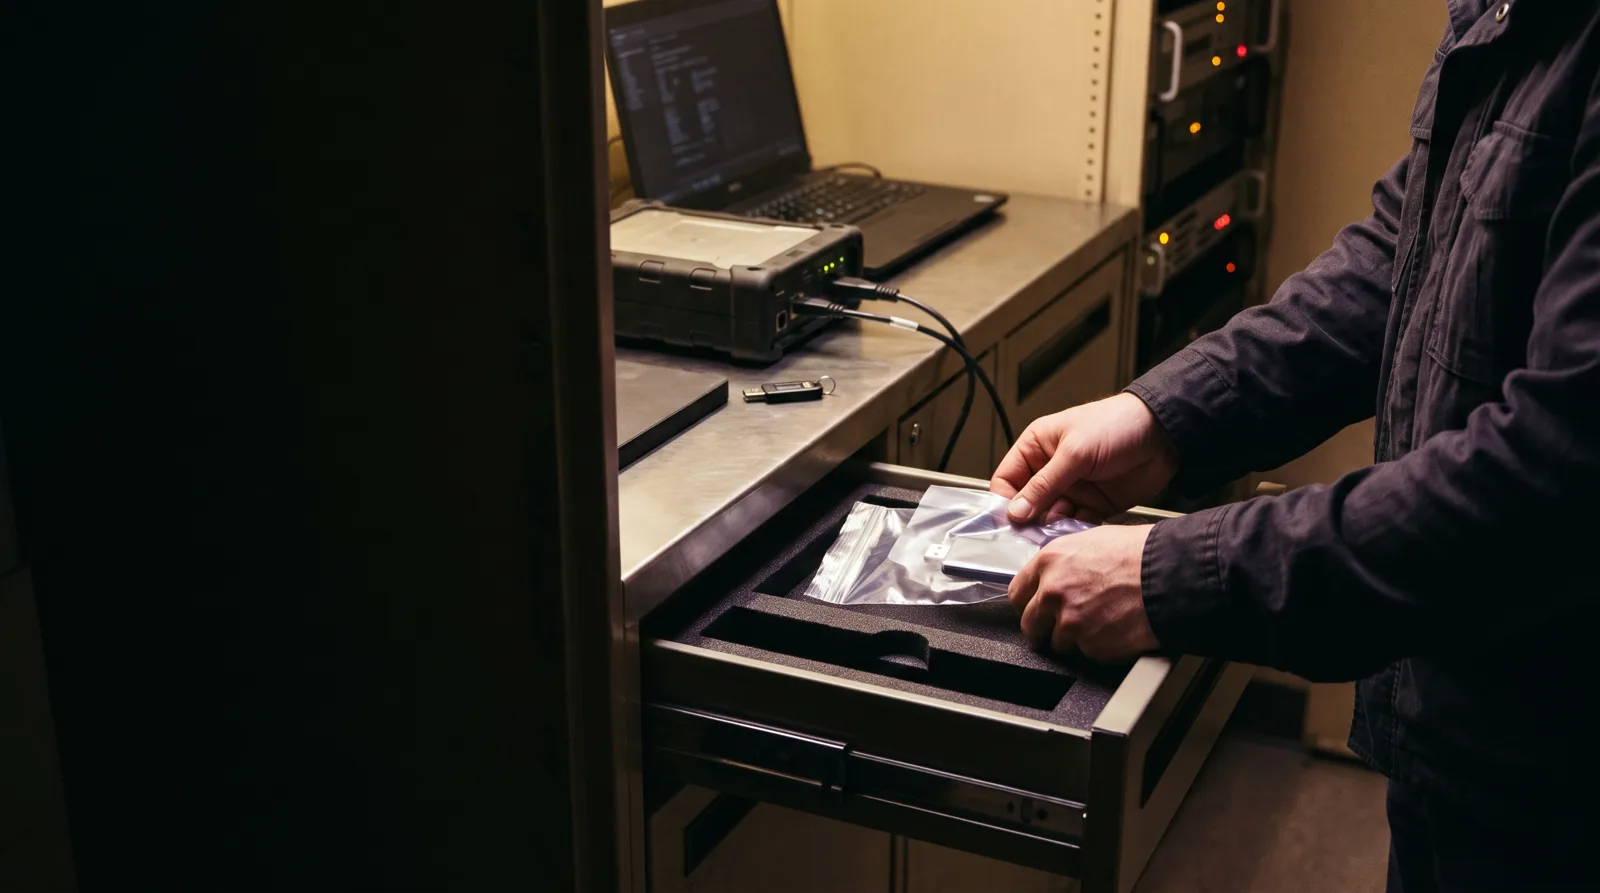
Who handed it over, where and at what time.
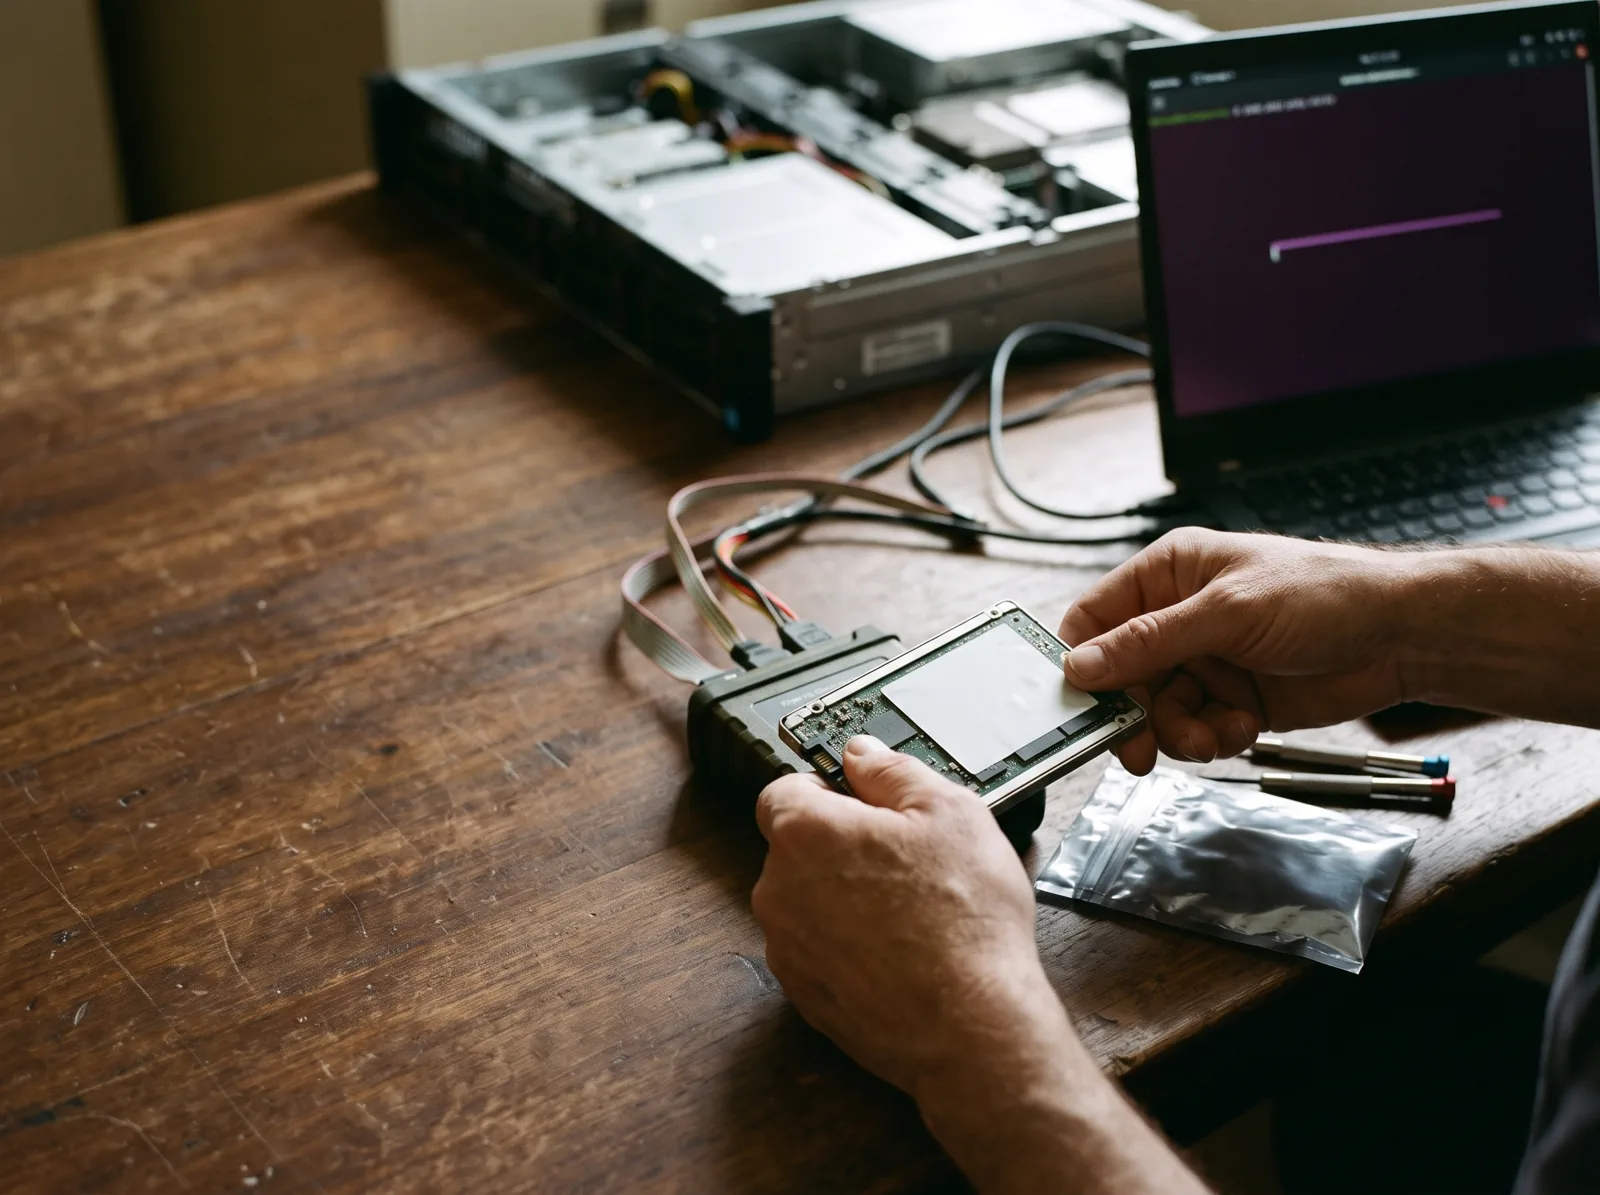
Imaged through a write blocker. The original is not opened.
SHA-256 of source and copy, compared and logged.
Original bagged, numbered and locked away.
Returned or destroyed, with a signature for either.
Disk and memory copies, encrypted at rest
Case notes and the evidence log
Final report, one copy
Legal hold, if your counsel asks
The report cites these as it goes, so your auditor can follow any finding back to the standard behind it.
Stage | Reference | What it shows in the report |
Triage | NIST SP 800-61, ISO/IEC 27035 | Scope, severity and who decided what. |
Contain | NIST SP 800-61, RFC 3227 | What was isolated, in what order, and why. |
Investigate | ISO/IEC 27037, MITRE ATT&CK | The evidence log and each attacker step, named. |
Report | NIST Cybersecurity Framework 2.0 | What changed and what comes next, by function. |
A full report from a sample case, names removed. Scope, timeline, findings by severity, what changed.
One-page summary for the board
Timeline, host by host
Findings by severity
Evidence log with hashes
What to change first