No handoffs to a second tier. The name on the first note of your case is the name on the last page.
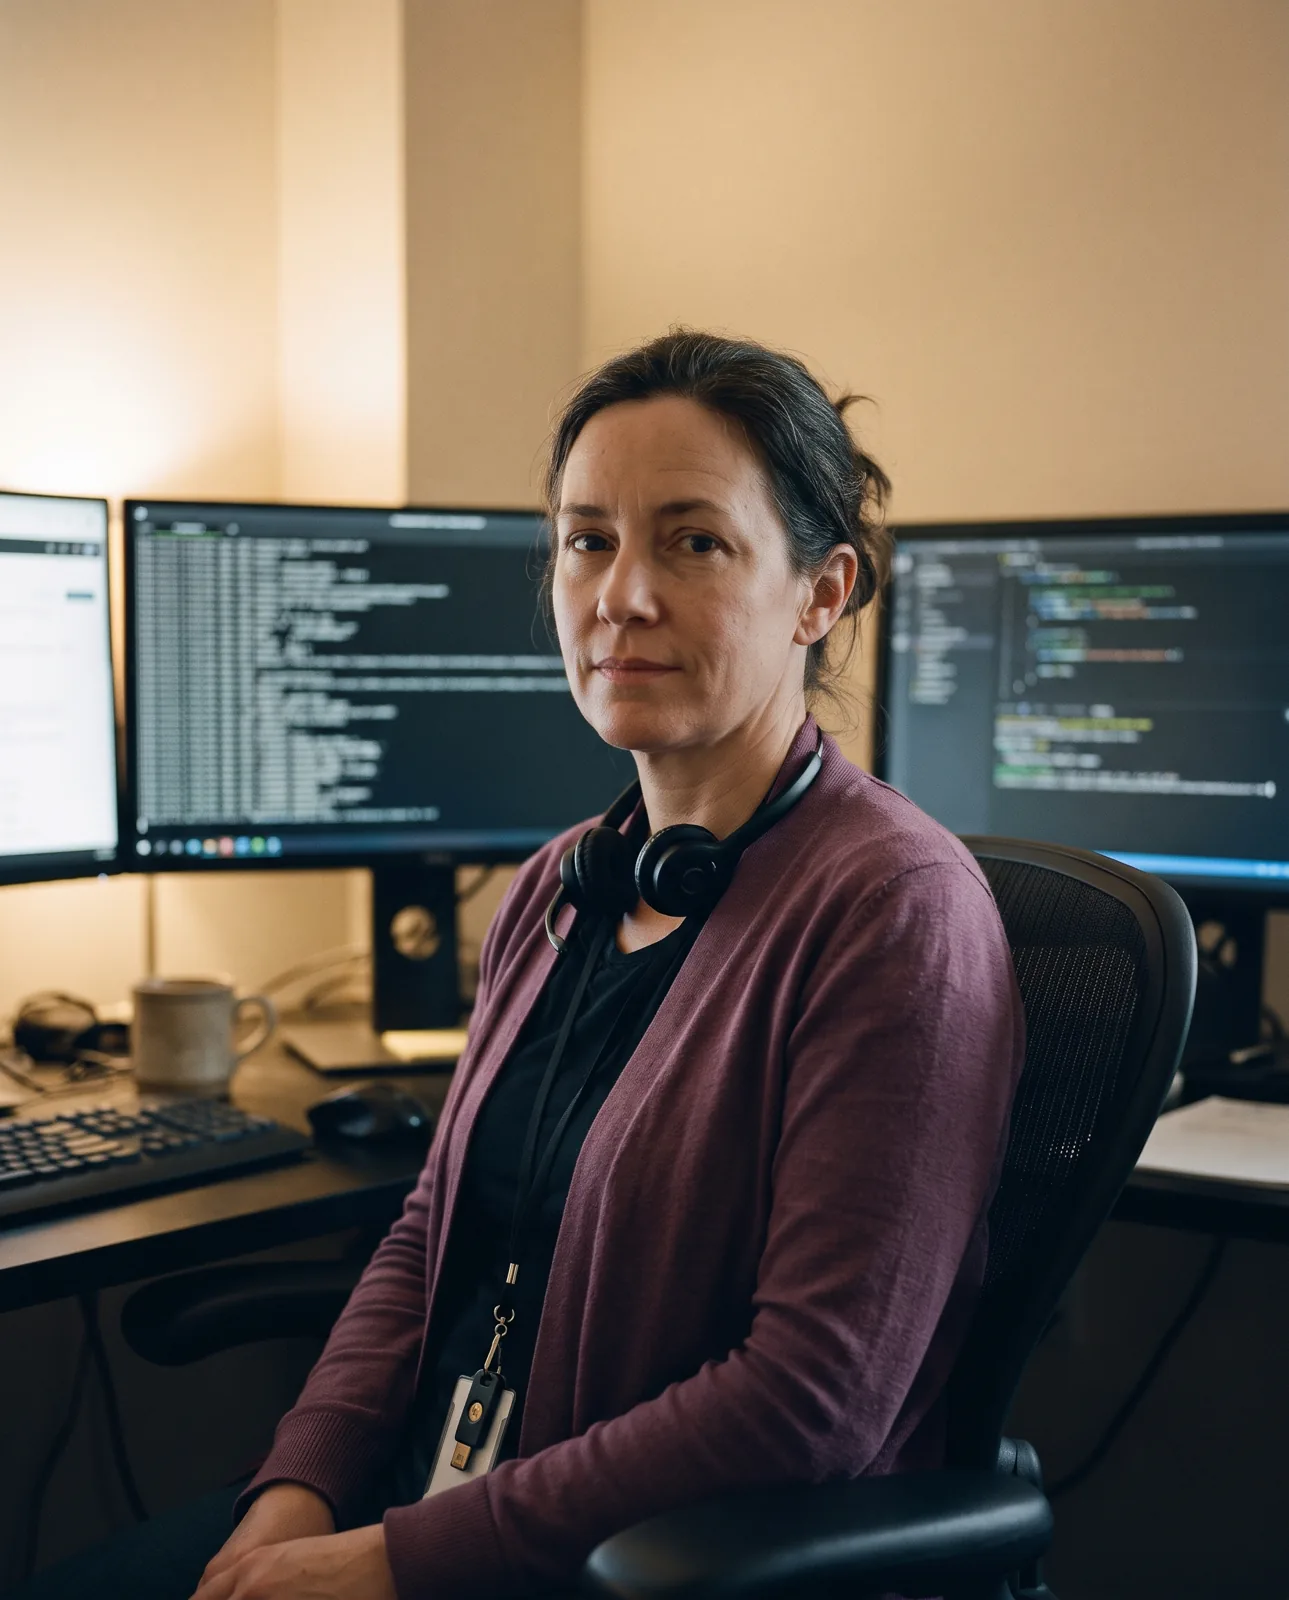
Mara founded Wardline after years answering incident calls. She still runs a case most weeks, and reads every report before it leaves the building.
Credentials | GCFA, CISSP |
At Wardline since | 2015 |
Last case led | WL-26-114 |
Home number | number withheld |
Each one leads a part of the record. Disks, code and the room itself.
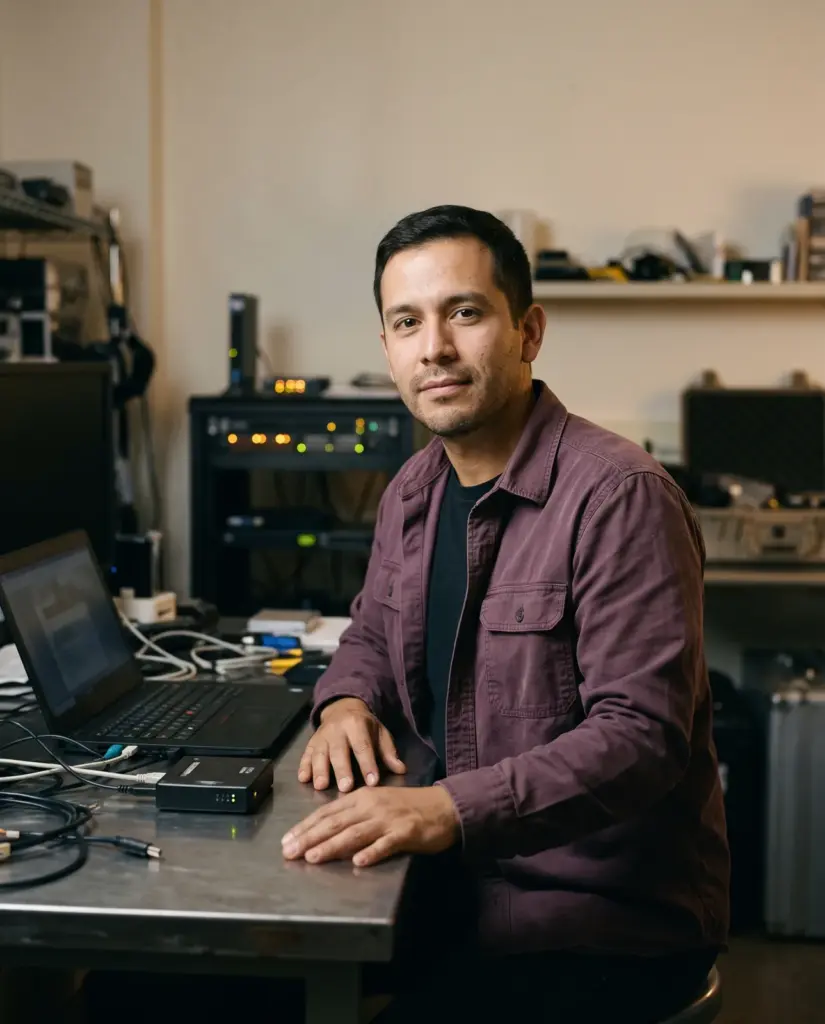
Built the evidence log. Reads a disk the way other people read a diary. GCFE, GCFA
Takes apart what we find on a case and writes the research desk’s briefs. GREM
First through the door on site. Isolates hosts by hand when the network cannot be trusted. GCIH
Also on the rota: Priya Raman, Jonas Weller, Hana Novak, Owen Achebe and seven more. Sample team for this demo.
You will know each person by name before they touch a system.
Agrees the scope and opens the record.
Goes on site, or works remotely with your IT lead.
Copies and hashes disks, memory and logs.
Works out what the tooling did and what else it could reach.
Signs the last page and walks you through it.
GIAC Certified Forensic Analyst
GIAC Certified Forensic Examiner
GIAC Reverse Engineering Malware
GIAC Certified Incident Handler
Certified Information Systems Security Professional
Four roles are open in this issue, including one for someone starting out.