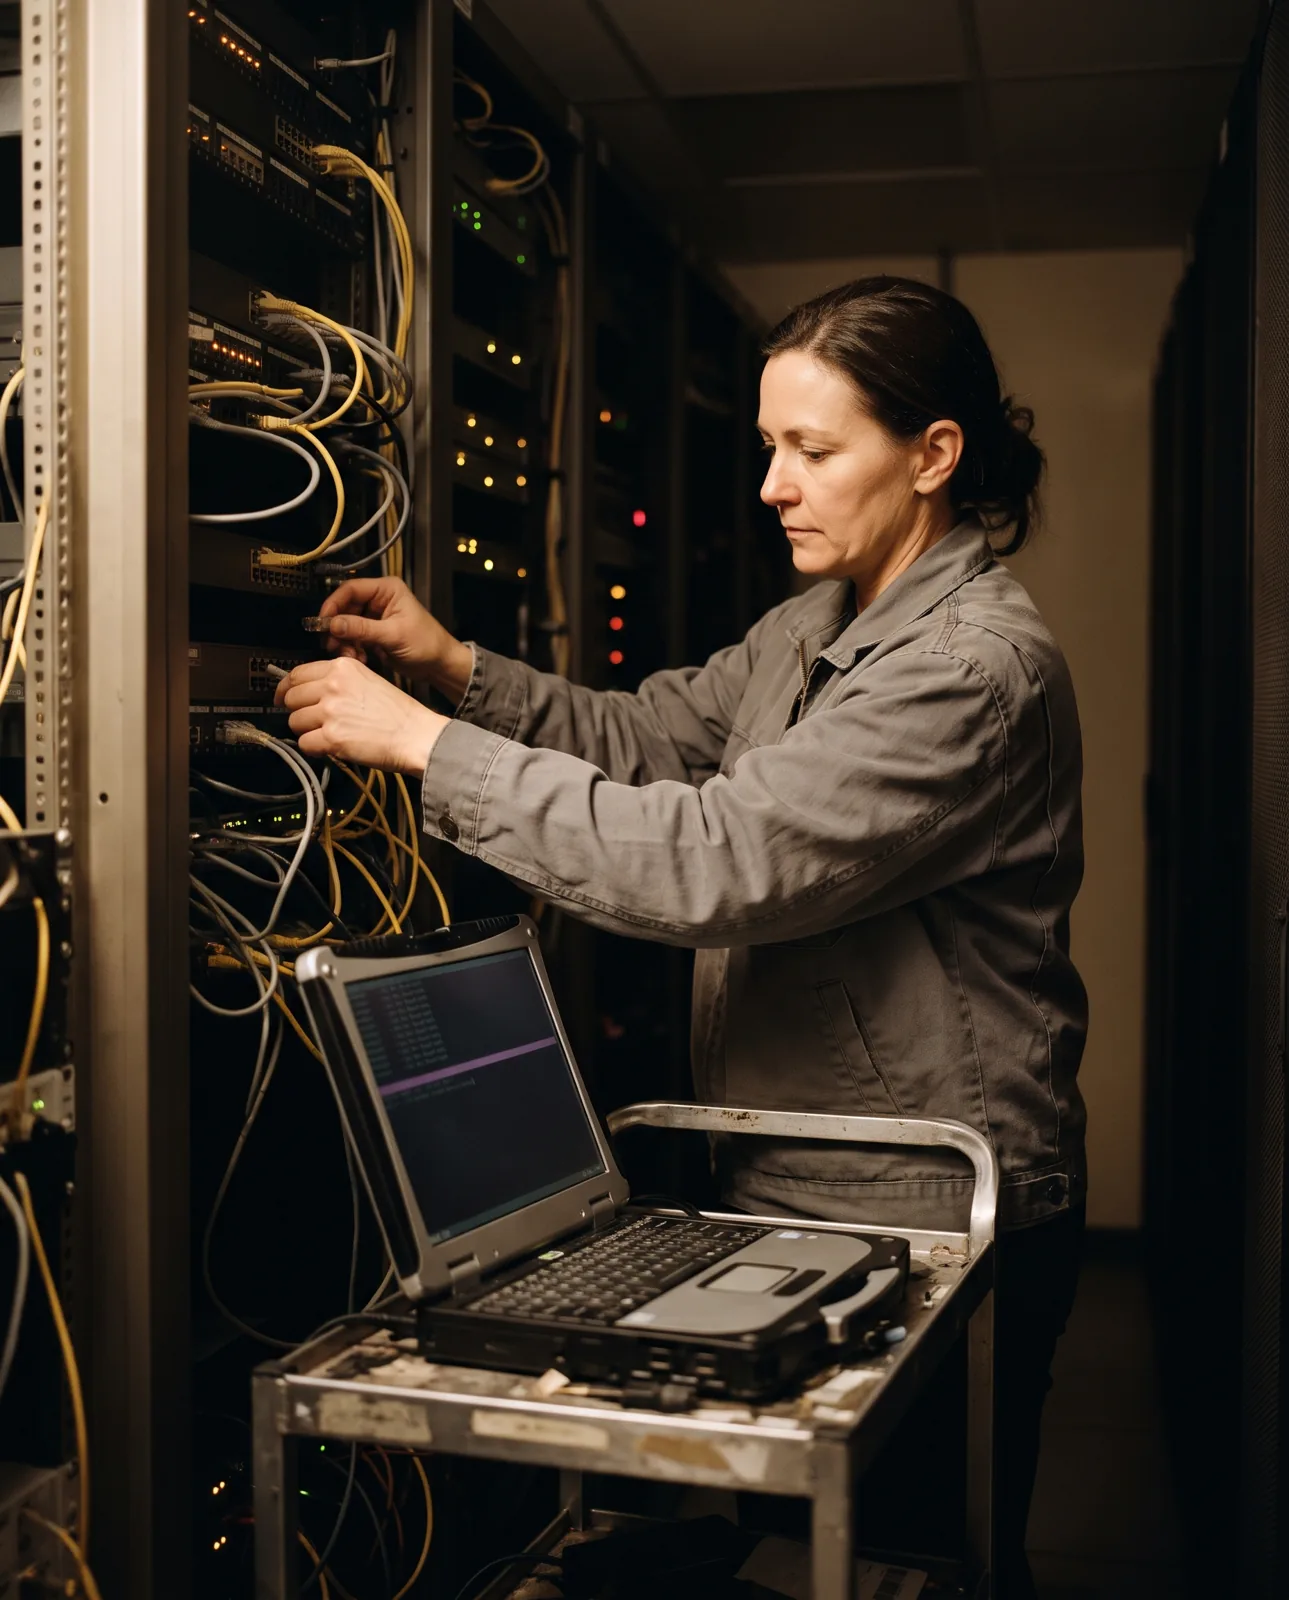
Ransomware crews stage before they encrypt. This is what that week looks like in the logs: very little, and in a place nobody watches.
Backups are the target because they are the way out. A crew that can reach the backup host can decide when recovery stops being possible.
What we saw in the sample case
- An admin sign-in at an hour that account never used.
- A new scheduled task with a dull name.
- Tools copied in, then left alone for days.
- Small test deletions of old backup sets.
The loud part takes an hour. The quiet part takes a week.
Stopped before encryption
In the sample healthcare case the response team contained it in 3 h 40 min, and nothing was encrypted. Keep one backup copy offline, and alert on any sign-in to the backup host, because normal use of that host is rare.