Penetration tests and red team exercises for companies that would rather hear it from us. Every finding comes with proof, a fix and a free retest.
from first packet to domain admin
Each case study reads like the report the client received: scope, severity counts, how far we got and what changed after.
Scope, test windows and a stop contact, all signed before anything starts.
We map what the internet can see and what your staff already expose.
One weak point is enough. We log the time and exactly how it worked.
We move toward the goal you named, and stop at proof.
Nothing runs outside the signed scope. Your named contact can stop the test at any time with one phone call.
Findings, proof and fixes, read through with your team on a call.
Every Critical and High is run again, and you get the result in writing. Our work follows NIST SP 800-115 and PTES, with findings scored in CVSS.
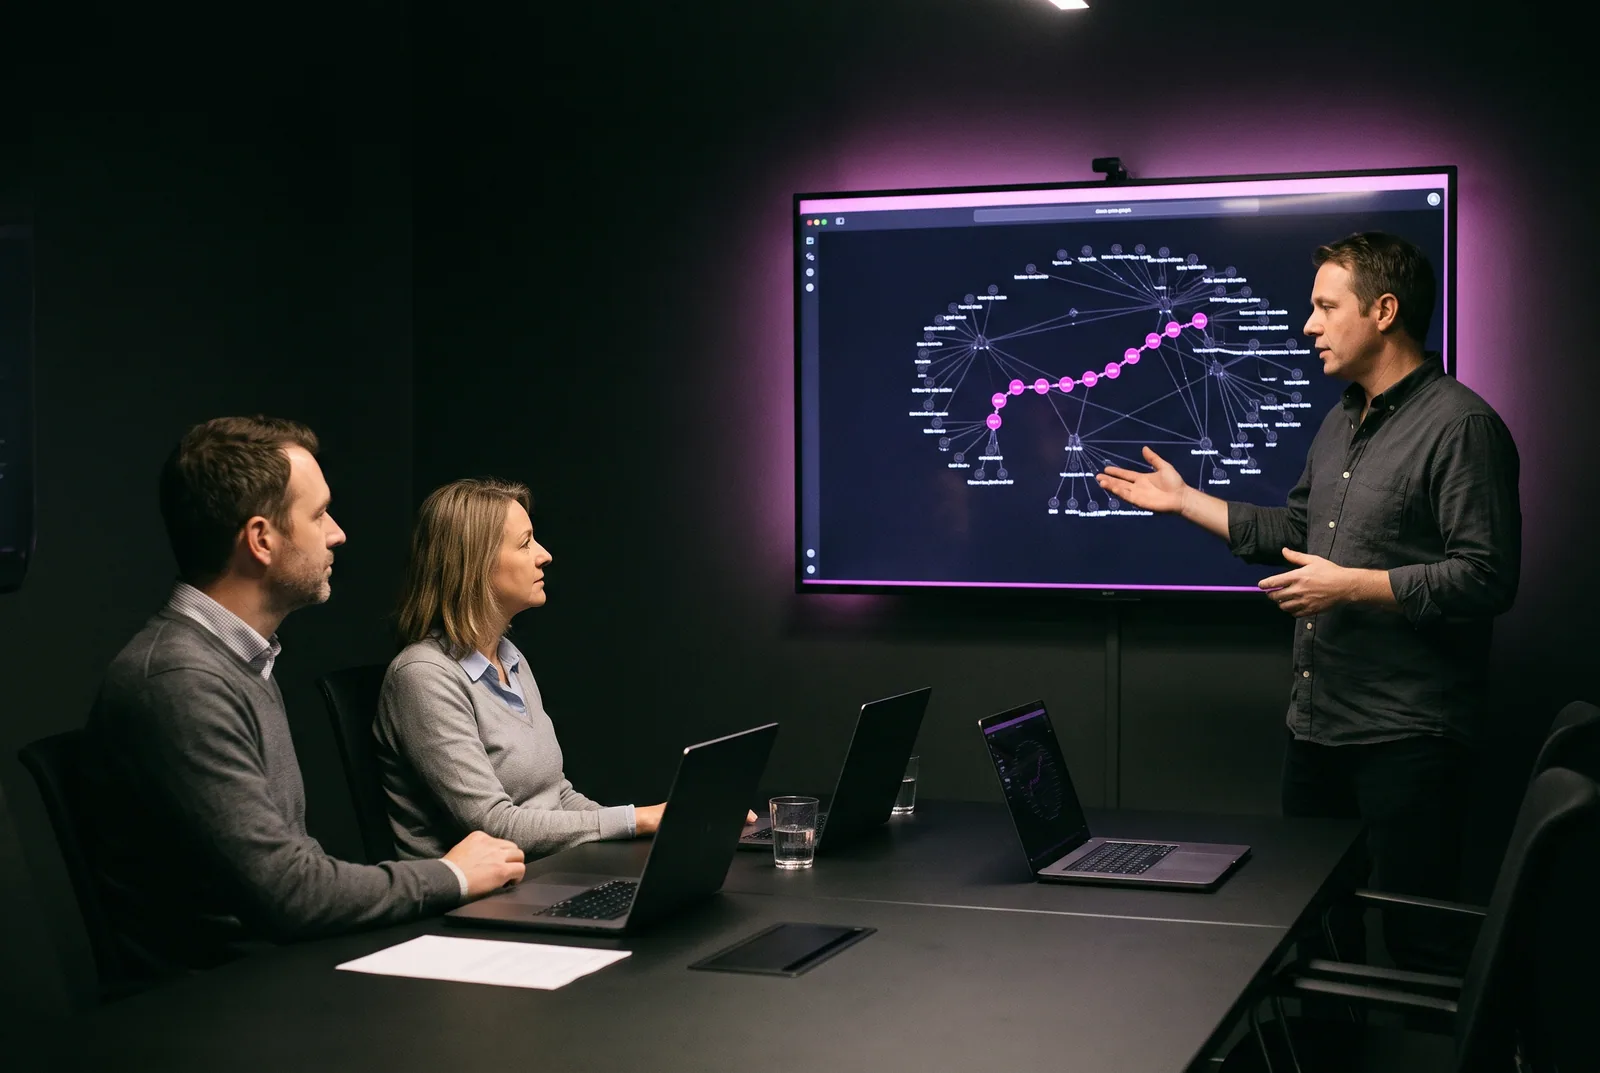
The same format your board would get. We send it by email, with no sales call attached.
Rather talk? +1-555-0187 · [email protected]
Thirty minutes with a tester, not a salesperson. You get a written scope and a fixed price within two working days.
We ask what you want to protect and why.
You get the scope, the price and the testers' names.
You sign the rules. We book the dates.