Healthcare security and compliance
§1Questions
Asked by privacy officers, IT leads and clinical engineering on a first call. If yours is missing, ring us and ask a person.
§2Agreements and patient data
A business associate agreement comes first on every plan. Your counsel reviews it with the scope note.
Yes, before any work starts, on every plan. It sits alongside the scope note, and your counsel reviews both.
We plan the work so we do not need to. We read network and system records, and we agree the access list with your privacy officer first.
In your systems. Our working notes stay in an encrypted store, and we delete them when the engagement ends unless you ask us to keep them.
Please. We bring the facts and the timeline. Your counsel confirms what applies to you.
§3Medical devices
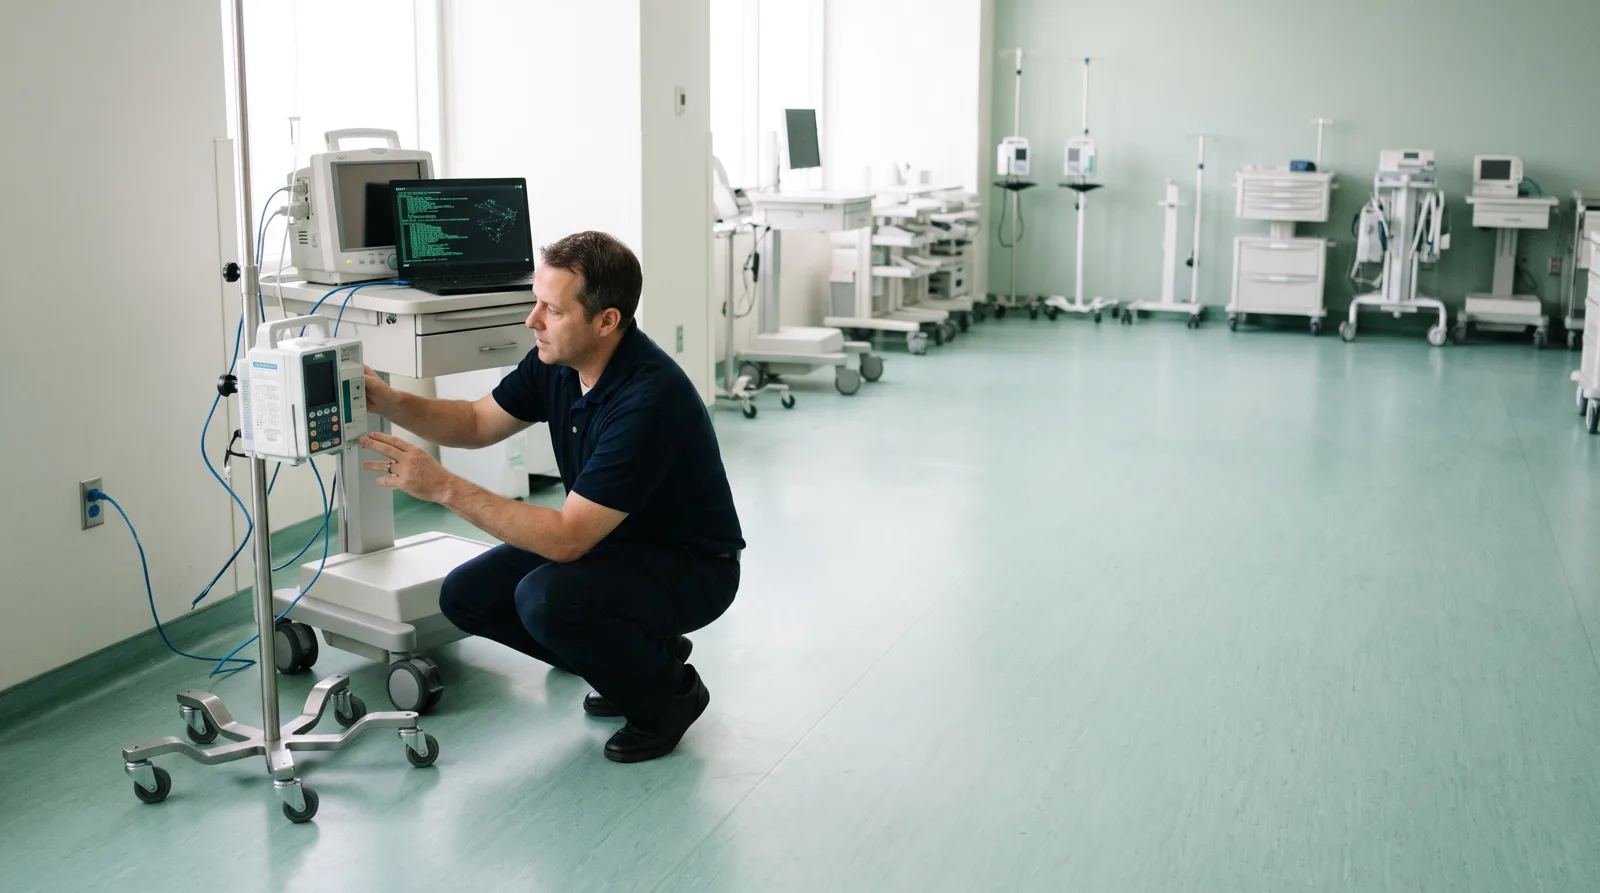
changes we make to device software. That stays with the vendor and clinical engineering.
No. That stays with the vendor and clinical engineering. We give each device class a safe place on the network.
With clinical engineering, unit by unit. A network scan finds a device; your engineers tell us what it is and who owns it.
They go on vendor hold and on their own network segment, with vendor access by request only.
Not if we do our job. Every move runs in a window the unit agreed, with a rollback written before the change.
§4Change windows and downtime
Unit | Window |
Emergency department | None. One side of the failover pair at a time. |
Intensive care | 02:00 to 04:00 |
Imaging | 00:00 to 04:00 |
Pharmacy | 02:00 to 06:00 |
Laboratory | 04:00 to 06:00 |
Outpatient clinics | 20:00 to 06:00 |
Sample schedule, demo data. Yours is set with nursing and clinical engineering.
The unit manager, with nursing and clinical engineering. Victor Lindgren writes it down, and nothing moves without it.
We wait. The charge nurse can stop any change, and we come back the next agreed night.
Yes, with the units that rely on the failover. Grace Holloway runs them and writes the report the same night.
In our sample client record: 0 minutes in twelve months, across 1,284 changes, 6 of them rolled back inside the window.
§5Breaches and the 60 days
calendar days after discovery. Our plan finishes at 30.
Day 0Discovery logged, privacy lead told
Day 2Four-factor risk assessment starts
Day 10Scope confirmed with counsel
Day 30Notices ready, HHS and media if 500 or more
Sample runbook, not legal advice.
Your privacy officer and counsel. We bring the facts and the timeline, so they can make the call.
The rule asks for no unreasonable delay. Sixty days is the outer limit, not a target, so our plan leaves room.
In sample case CS-05, a specialty clinic ran two tabletop sessions. Steps with no owner went from 7 to 0.
Yes. Ring +1-555-0187 at any hour. The person on call has read your runbook.
§6Plans and cost
Clinic$2,400, up to 3 sites
Hospital$7,800, one hospital
Group$14,500, several hospitals
Sample pricing, demo data.
The six jobs on our home page, sized to your sites: risk analysis, device inventory, network segments, hardware keys, downtime drills and breach readiness.
No. The first month starts with the risk review, and the price is the same as every other month.
Hardware, such as the keys themselves, and new network equipment. We quote those first, and you say yes before anything is ordered.
Give sixty days' notice. You keep every report, register and runbook, and we hand over the access list.