Healthcare security and compliance
§1Wardline healthcare
Security and compliance work for hospitals and clinics. We look after medical devices, close HIPAA Security Rule gaps and change nothing while a unit is busy.
§2Change windows
Each unit agrees its own window with us before anything moves. Outside it, we watch and we wait.
§3Medical devices
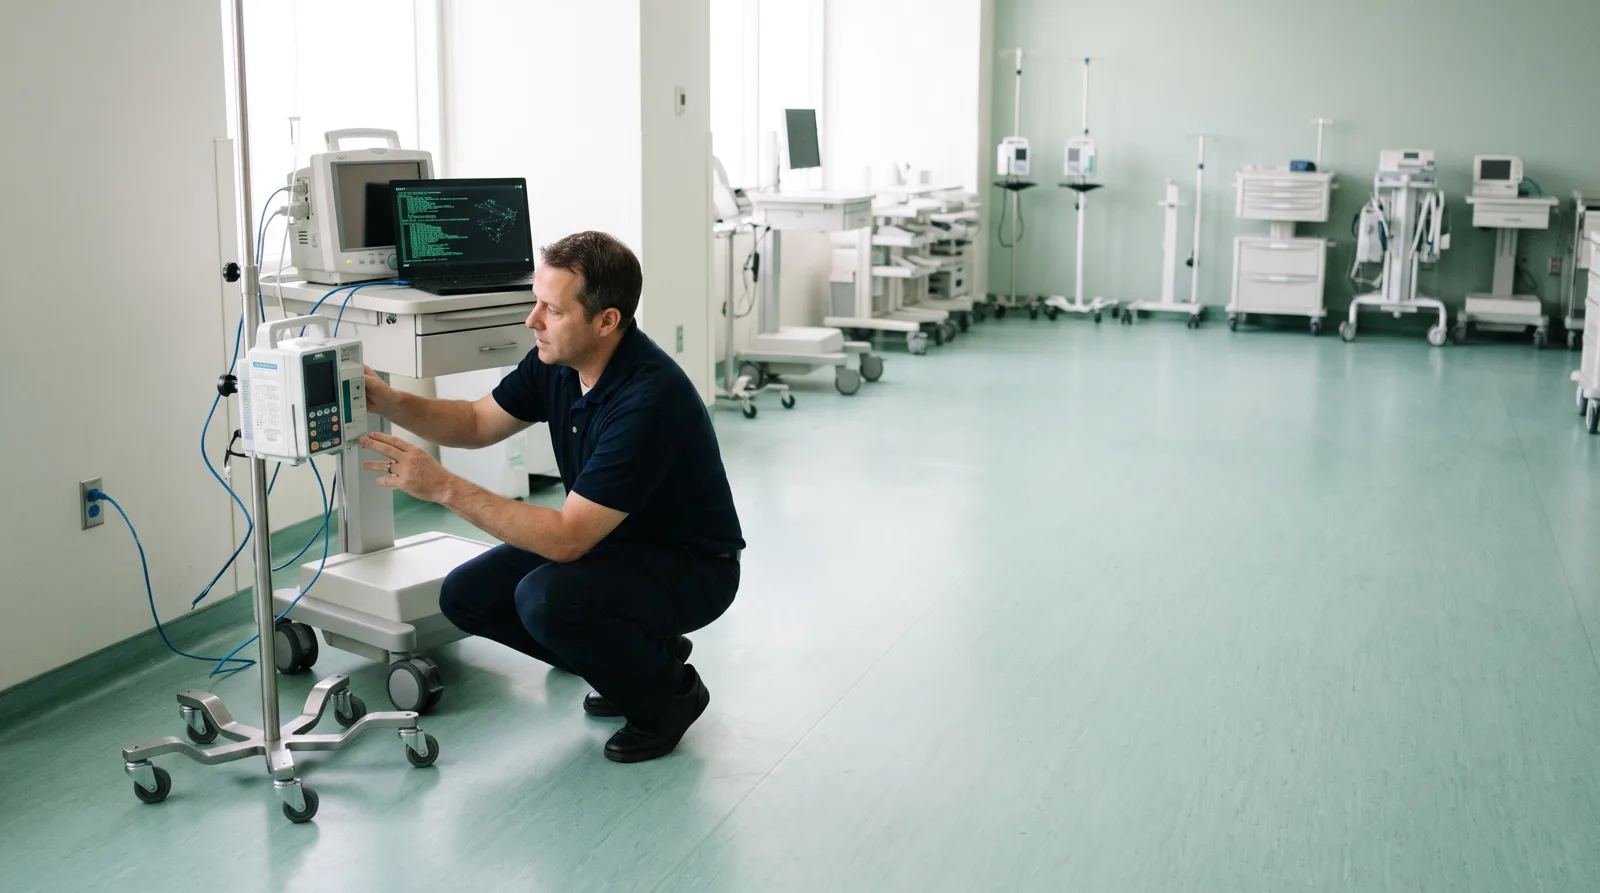
We count every connected device with clinical engineering, then give each class a safe place on the network. The device stays cleared and unchanged.
Device class | On network | Vendor hold | Action |
Infusion pumps | 1,860 | 212 | Pump segment |
Patient monitors | 940 | 64 | Unit segment |
Imaging systems | 62 | 31 | Vendor access by request |
Lab analyzers | 118 | 11 | Lab segment |
Nurse call and badges | 1,232 | 0 | Patched in window |
Total | 4,212 | 318 |
§4Two rules
Risk analysis, staff training, contingency plans.
Facility access, workstation use, device and media controls.
Access control, audit controls, transmission security.
Day 0Discovery logged, privacy lead told
Day 2Four-factor risk assessment starts
Day 10Scope confirmed with counsel
Day 30Notices ready, HHS and media if 500 or more
Sample runbook, not legal advice. Your counsel confirms what applies.
§5What we run
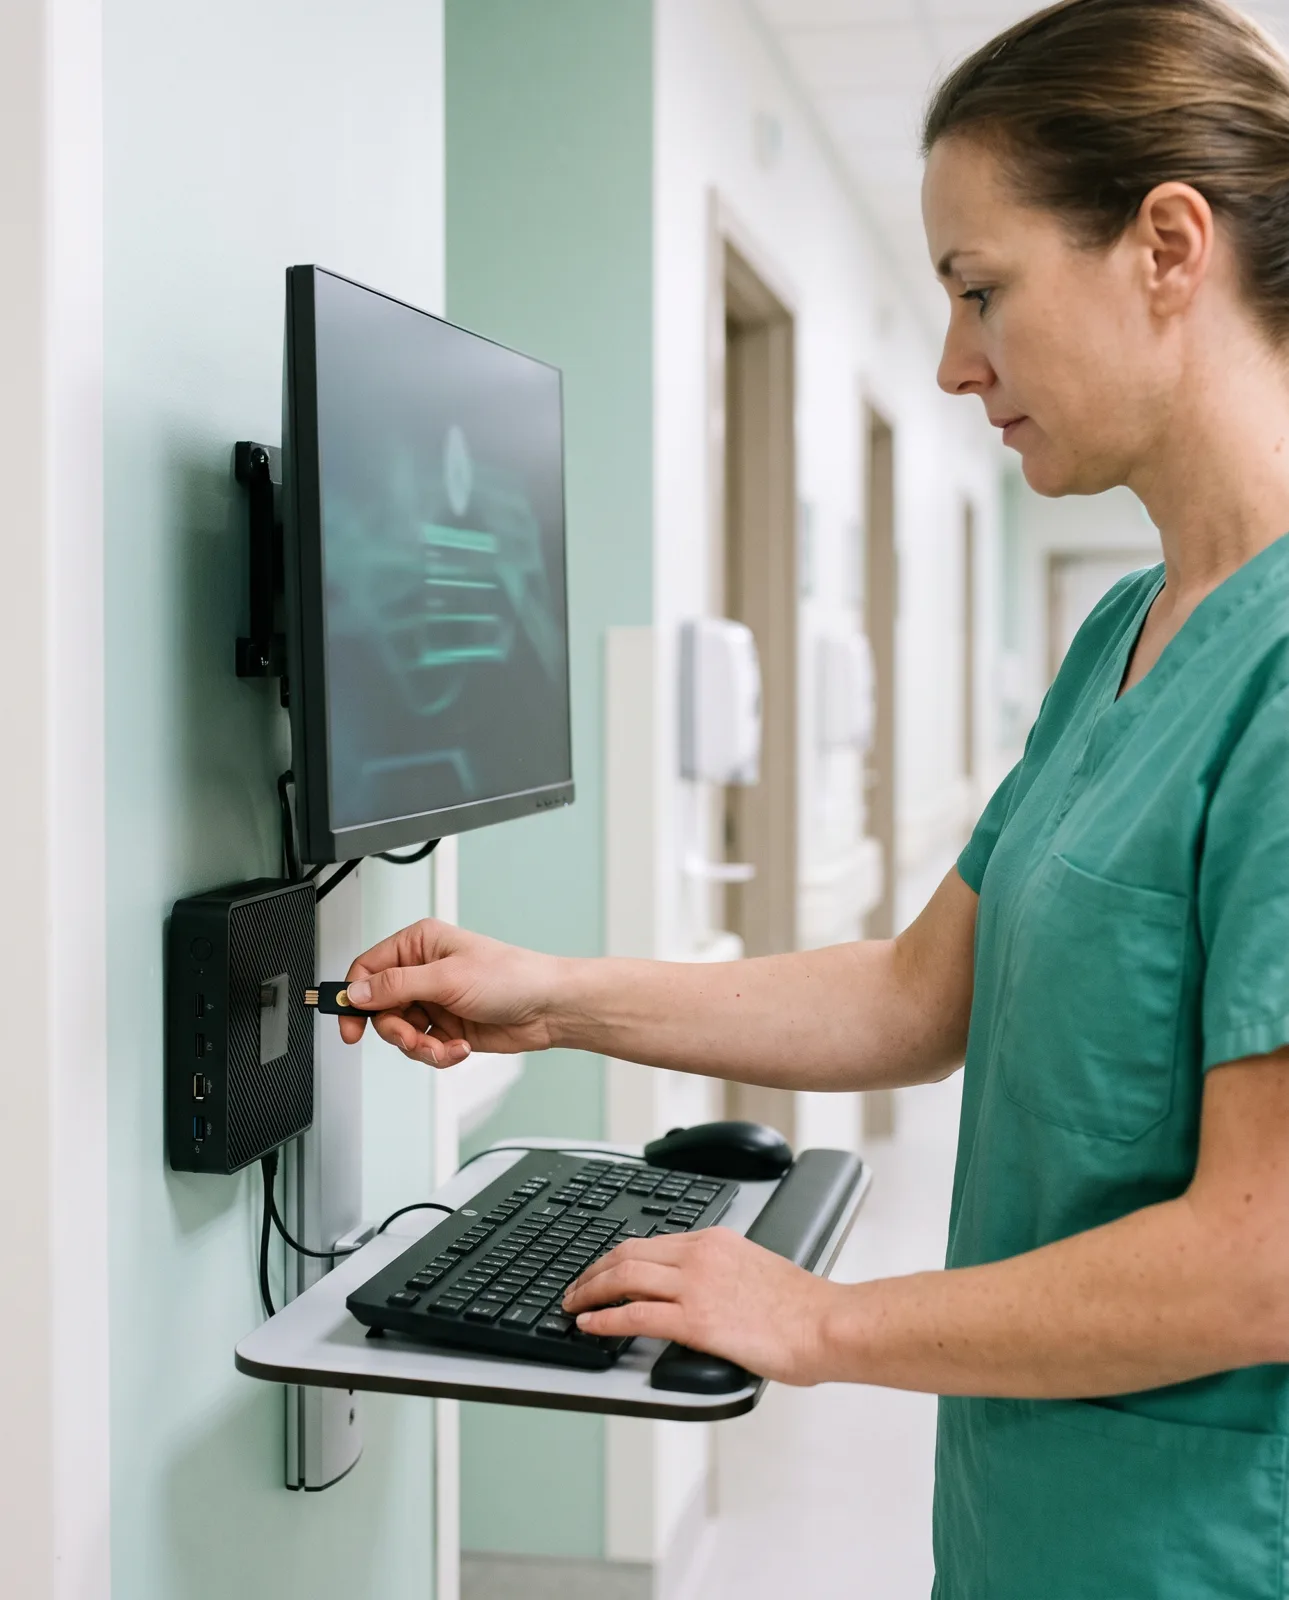
Shared logins end. The shift keeps its pace.
§6Case study
Sample case, fictional client
SectorRegional hospital group, 3 sites
ScopeClinical network failover, 6 units
FindingsCritical 2
High 9
Low 31
To contain38 minutes, drill
ResultRisk analysis closed out, demo sample
§7Questions
Privacy officer, regional hospital group. Sample quote, fictional person.
Yes, before any work starts. It sits alongside the scope note, and your counsel reviews both.
We plan the work so we don't need to. We read network and system records, and we agree the access list with you first.
No. That stays with the vendor and clinical engineering. We change the network around the device.
Your privacy officer and counsel. We bring the facts and the timeline, so they can make the call.
§8Contact